
9 UCaaS Providers for Regulated Organizations in 2026
The best UCaaS providers for regulated organizations are communication platforms that combine business calling, video meetings, messaging, and collaboration with verifiable security controls, communication retention, auditability, and appropriate contractual safeguards. Microsoft Teams Phone, Cisco Webex, RingCentral, Zoom, and 8×8 are among the cloud-based options worth evaluating. For organizations that require direct control over communication infrastructure or must operate in isolated networks, an on-premises alternative such as TrueConf Server may be more suitable than conventional UCaaS.
Healthcare providers, financial institutions, government agencies, legal organizations, and companies operating critical infrastructure cannot select unified communications software based on features and subscription prices alone. They must understand where communication data is processed, how conversations are recorded and retained, who can access administrative systems, and whether the provider supports applicable regulatory obligations.
No UCaaS provider is automatically compliant with every regulation. A vendor may offer HIPAA-related contractual safeguards, SOC 2 reports, FedRAMP-certified services, or financial communication archiving integrations, but these capabilities can apply only to specific products, environments, configurations, or subscriptions. The appropriate choice depends on the organization’s regulatory obligations, data sensitivity, operational requirements, and acceptable level of third-party dependence.
Best UCaaS Providers for Regulated Organizations at a Glance
|
Provider |
Deployment model |
Relevant capabilities |
Best suited for |
|---|---|---|---|
|
Cloud UCaaS |
Purview retention, eDiscovery, DLP, third-party compliance recording |
Microsoft 365 enterprises, finance, regulated professional services |
|
|
Cloud UCaaS, government-specific offerings |
FedRAMP-certified government suite, calling, messaging, meetings |
Government agencies and large regulated enterprises |
|
|
Zoom Workplace and Zoom Phone |
Cloud UCaaS, dedicated government offering |
Healthcare BAA, meeting archiving, Zoom for Government, administrative controls |
Healthcare, government, distributed organizations |
|
Cloud UCaaS |
SOC 2 assurance, communication exports, retention tools, compliance integrations |
Financial services and multi-location enterprises |
|
|
Cloud UCaaS |
Calling, meetings, messaging, analytics, security attestations |
Regulated businesses requiring integrated telephony |
|
|
On-premises UC alternative |
Private deployment, offline operation, directory integration, ICAP DLP integration |
Restricted networks, government, industrial environments |
|
|
Dialpad Connect |
Cloud UCaaS |
Business calling, messaging, AI features, healthcare BAA |
Healthcare teams and AI-enabled business communication |
|
Vonage Business Communications |
Cloud UCaaS |
Business telephony, recording policies, SSO, 2FA, centralized administration |
Regulated organizations requiring flexible communication workflows |
|
GoTo Connect |
Cloud UCaaS |
Cloud PBX, meetings, messaging, administrative controls, healthcare guidance |
Multi-site healthcare and professional services |
The main architectural distinction is control: a financial firm may need cloud-based recording and supervision, while an isolated industrial site needs communications that remain available without internet access. Compare vendors against actual regulatory requirements and business workflows, not generic security labels.
Which UCaaS Provider Should You Choose?
For financial services, Microsoft Teams Phone and RingCentral are useful starting points because they offer documented approaches to communication recording, retention, and integration with compliance systems. Cisco Webex and other enterprise platforms may also be suitable, but recording coverage and supervisory workflows must be verified for the intended channels.
For healthcare, Zoom, Dialpad, 8×8, and GoTo Connect offer relevant healthcare-oriented services or contractual arrangements. Their suitability depends on the availability and scope of Business Associate Agreements, protected health information handling, recording configurations, and enabled AI functionality. Microsoft Teams can also support healthcare environments through appropriate Microsoft 365 agreements and controls.
For government and restricted infrastructure, Cisco Webex for Government and Zoom for Government provide dedicated cloud environments with FedRAMP certification. Microsoft also offers government cloud environments that require separate evaluation. Where public cloud connectivity is prohibited or communication must remain inside a controlled network, TrueConf Server provides an on-premises alternative rather than conventional UCaaS.
For organizations prioritizing integrated calling and customizable workflows, 8×8, Vonage, and GoTo Connect provide additional options. The final decision should be based on demonstrated coverage of regulated communication activities, not the provider’s general industry positioning.
What Is UCaaS for Regulated Organizations?
Unified Communications as a Service (UCaaS) is a cloud delivery model that provides multiple business communication functions through a managed subscription service.
A typical UCaaS platform combines enterprise telephony, video conferencing, team messaging, presence information, voicemail, and communication administration. Many providers also offer contact center integrations, workflow automation, analytics, and AI-assisted features.
For regulated organizations, UCaaS must do more than connect employees. It must fit into an environment where communications may be subject to privacy requirements, records retention obligations, supervisory review, incident reporting, or restrictions on data processing.
For example, a financial institution may need to retain certain business communications for examination. A healthcare organization may exchange protected health information during patient consultations. A government agency may have strict requirements concerning the certification of cloud services and the handling of sensitive records.
The feature set may be similar, but the required safeguards differ.
What Makes Regulated UCaaS Different From Standard UCaaS?
The main difference is the level of assurance the organization needs about the handling of communication data.
Standard UCaaS buyers often prioritize calling quality, ease of use, integrations, and subscription costs. Regulated organizations must also evaluate whether the platform supports appropriate retention periods, access restrictions, recording policies, evidence preservation, audit trails, approved processing locations, and contractual commitments.
These obligations shape procurement, deployment, administration, and exit planning.
UCaaS vs. On-Premises Unified Communications
Cloud UCaaS and on-premises unified communications can offer similar end-user experiences, but their infrastructure responsibilities differ.
|
Criterion |
Cloud UCaaS |
On-premises unified communications |
|---|---|---|
|
Hosting |
Provider-managed infrastructure |
Organization-managed or dedicated infrastructure |
|
Software maintenance |
Primarily provider responsibility |
Primarily customer or managed service responsibility |
|
Infrastructure ownership |
Limited customer control |
Direct customer control |
|
Data location |
Depends on provider services and contractual options |
Determined by deployment architecture |
|
Internet dependency |
Usually required for core cloud services |
Can be avoided for internal communication when supported |
|
Communication retention |
Native functions or supported archiving integrations |
Depends on product capabilities and customer systems |
|
Scaling |
Subscription and provider capacity |
Available infrastructure and licensing |
|
Security operations |
Shared responsibility |
Greater direct operational responsibility |
|
Regulatory suitability |
Depends on service certification and configuration |
Depends on deployment, controls, and applicable requirements |
Neither architecture is automatically more secure.
Cloud UCaaS can provide sophisticated security operations, geographic redundancy, and compliance integrations. On-premises deployment offers more direct infrastructure control but requires the organization to manage security, maintenance, monitoring, and business continuity.
Insight 1. Regulatory Compliance Is a Property of the Deployment, Not Just the Provider
A vendor’s compliance certification or audit report does not mean every customer automatically meets the same requirements.
A UCaaS provider may undergo a SOC 2 audit, but the report can apply only to defined services and controls. A healthcare organization may sign a Business Associate Agreement, but it must still configure appropriate access, recording, and information handling policies.
Similarly, FedRAMP certification applies to a specific cloud service offering and certification boundary, not automatically to every commercial product sold by the same company.
The correct evaluation question is not simply whether a UCaaS provider is compliant, but whether the exact proposed service, configuration, contract, and operating model support the organization’s obligations.
Which Regulations Matter When Choosing UCaaS?

Regulated organizations face different obligations depending on their industry, location, information categories, and business activities.
A compliance requirement may apply to messages, recordings, metadata, access logs, contractual arrangements, or the provider’s infrastructure.
HIPAA for Healthcare Organizations
The Health Insurance Portability and Accountability Act establishes requirements relevant to the protection of health information in covered U.S. healthcare environments.
A UCaaS provider handling electronic protected health information on behalf of a covered entity may need to enter into a Business Associate Agreement.
However, a BAA does not make every application setting appropriate for protected health information.
Healthcare organizations must evaluate access controls, administrative permissions, recording policies, data transmission, retention, and any AI features that process sensitive content.
They should also determine whether telephone calls, video consultations, chat messages, voicemail, faxes, and transcripts are covered by the proposed service arrangements.
FINRA, SEC, and Financial Communication Supervision
Financial institutions may be required to preserve and supervise particular business communications.
Relevant obligations can include SEC books and records rules, FINRA supervision requirements, and other recordkeeping obligations determined by the firm’s activities.
A communication platform may provide recording or export functionality without delivering a complete compliant archiving and supervisory review system.
For example, a normal meeting recording stored in an employee’s workspace is not necessarily equivalent to a policy-controlled compliance recording captured into an archive of record.
Organizations should verify whether approved communications can be captured, preserved, searched, reviewed, and produced according to their actual obligations.
GDPR and Data Protection Requirements
The General Data Protection Regulation applies to relevant processing of personal data.
When evaluating UCaaS, organizations should consider the legal basis for processing, appropriate contractual arrangements, security measures, international transfers, data subject rights, and retention practices.
Data residency can be relevant, but storing information in an EU data center does not automatically establish GDPR compliance.
The organization must also understand subprocessors, administrative access, backups, recordings, and whether customer content is processed by additional AI services.
DORA for EU Financial Institutions
The Digital Operational Resilience Act applies to covered EU financial entities and establishes requirements concerning ICT risk, operational resilience, incident management, testing, and third-party risk.
UCaaS can become relevant to DORA assessments when communication services support important business operations.
Organizations should assess provider dependencies, contractual commitments, service continuity, incident notification, and exit arrangements.
Where ICT services support critical or important functions, additional requirements may apply.
FedRAMP Certification and U.S. Government Cloud Services
FedRAMP provides a government-wide framework for assessing and certifying cloud services intended for use by U.S. federal agencies.
In 2026, FedRAMP introduced updated certification terminology.
Under the 2026 terminology update, FedRAMP Certified is the standard status label used by the Marketplace, while FedRAMP Authorized remains familiar from earlier documentation. The certification framework also uses Classes A, B, C, and D to describe assessment requirements. This change in terminology does not invalidate existing authorizations.
Under the transition model, Class B corresponds broadly to the former Low baseline, Class C corresponds to Moderate, and Class D corresponds to High. Class A represents a new entry-level certification path.
These classes describe assessment and reporting requirements, not a universal ranking of a product’s overall security quality.
The legacy Revision 5 framework and the newer FedRAMP 20x approach coexist during the transition.
For example, Zoom for Government is listed in the FedRAMP Marketplace as a Rev5 offering with Class C (Moderate) certification.
The transition also distinguishes between the certification of a cloud service offering and an agency’s decision to grant an Authority to Operate or Authority to Use for its own implementation.
Government organizations should verify the specific service’s current FedRAMP status, certification class, framework type, and scope in the official marketplace.
The terminology change does not eliminate the need for agency-specific authorization, security review, or appropriate configuration.
Industry-Specific Requirements
Other regulations and standards may affect communication systems, including MiFID II, PCI DSS, state privacy laws, and sector-specific cybersecurity frameworks.
Requirements can also differ across jurisdictions within the same organization.
A multinational business should therefore assess the exact obligations applicable to each communication workflow rather than assume that a single global compliance label is sufficient.
UCaaS Compliance Requirements by Industry
|
Industry |
Primary concern |
UCaaS capabilities to evaluate |
|---|---|---|
|
Healthcare |
Patient confidentiality and protected health information |
BAA, access controls, secure consultation workflows, recording governance |
|
Banking and investment services |
Preservation and supervision of communications |
Compliance recording, archiving, eDiscovery, supervisory review |
|
Insurance |
Sensitive customer records and regulated transactions |
Identity management, recording retention, secure file sharing |
|
Government |
Certified cloud services and sensitive information |
Applicable FedRAMP certification boundary, access control, auditability, approved deployment |
|
Legal services |
Client confidentiality and evidence preservation |
Secure meetings, recording controls, retention, administrative access |
|
Energy and manufacturing |
Operational continuity and infrastructure restrictions |
Private deployment, redundancy, offline communication options |
|
Education and public healthcare |
Personal information and distributed communication |
Access controls, data protection agreements, retention policies |
|
EU financial entities |
ICT resilience and third-party dependencies |
DORA-related vendor assessments, continuity, contracts, exit planning |
The applicable obligations depend on the activity and data being processed, not simply the industry label.
Why UCaaS Security Matters in 2026: Latest Statistics?
Recent cybersecurity research highlights why regulated organizations must assess communication providers as part of their wider third-party risk programs.
According to Verizon’s 2026 Data Breach Investigations Report, published in May 2026, third-party involvement accounted for 48% of the breaches examined, up from 30% in the preceding report.
The report also found that vulnerability exploitation had become the leading initial access vector at 31%. These findings underline the risks associated with external dependencies and exposed software infrastructure.
IBM’s Cost of a Data Breach Report 2026 reported a global average breach cost of $4.99 million, an increase of 12% from 2025. IBM also found that extensive use of AI and automation in security operations was associated with average breach cost savings of $1.93 million compared with organizations that did not use these technologies.
|
2026 finding |
Reported result |
Relevance to UCaaS procurement |
|---|---|---|
|
Breaches involving a third party |
48% |
Evaluate provider dependencies and supplier risk |
|
Relative increase in third-party involvement |
60% |
Strengthen due diligence and contract oversight |
|
Breaches initially involving vulnerability exploitation |
31% |
Assess patching, exposure management, and service architecture |
|
Global average data breach cost |
$4.99 million |
Consider financial consequences of communication data exposure |
|
Annual increase in average breach cost |
12% |
Review security investments and incident preparedness |
|
Average savings associated with extensive security AI and automation |
$1.93 million |
Evaluate monitoring and response capabilities without assuming AI is automatically safe |
These findings describe cybersecurity risks across industries, not UCaaS-specific incident rates. They should inform supplier risk assessments rather than be interpreted as evidence that a particular communication platform is unsafe.
Insight 2. A Secure UCaaS Platform Can Still Create a Third-Party Concentration Risk
Consolidating calling, video meetings, messaging, and recordings into one provider simplifies administration, but can also increase dependence on a single service.
If a company uses the same vendor for external calling, internal collaboration, customer support, and communication records, one significant outage may affect several business processes simultaneously.
For a regulated organization, this is not merely an inconvenience. Service interruptions may affect customer assistance, emergency coordination, regulated operations, or the preservation of required communications.
UCaaS consolidation reduces operational fragmentation, but it can increase the consequences of provider failure unless continuity arrangements are designed around that dependency.
A realistic business continuity plan should test alternative communication methods, provider outages, and the availability of critical records.
Best UCaaS Providers for Regulated Organizations in 2026
The comparison covers eight cloud UCaaS services and TrueConf Server, an on-premises unified communications alternative for restricted infrastructure. Capabilities and assurance reports apply to specific products and configurations; the limitations below distinguish native features from partner integrations.
1. Microsoft Teams Phone
Best for: Enterprises using Microsoft 365 that need integrated collaboration, cloud telephony, retention, eDiscovery, and configurable compliance recording.
Microsoft Teams Phone extends Microsoft Teams with business telephony capabilities. It brings calling into the same environment as meetings, chat, file collaboration, and Microsoft 365 productivity applications.
For regulated organizations, the main attraction is the broader Microsoft security and compliance ecosystem.
Enterprise Calling and Collaboration
Microsoft Teams Phone supports cloud calling, call queues, auto attendants, voicemail, and organization-managed calling policies.
Organizations can connect the telephone network through available options such as Microsoft Calling Plans, Operator Connect, and Direct Routing, depending on geography and deployment.
Direct Routing is particularly relevant when an enterprise needs to retain selected existing telephony infrastructure or connect Teams to supported session border controllers.
Microsoft Purview Retention and eDiscovery
Microsoft Purview supports retention and eDiscovery across supported Microsoft 365 content.
Administrators can configure retention policies for Teams chats and channel messages. Files shared through Teams are stored in associated OneDrive or SharePoint locations and require the corresponding retention controls.
This distinction matters because a retention policy covering chat messages does not automatically govern every document, meeting recording, or transcript.
For investigations, supported content can be preserved and searched through the appropriate Microsoft Purview capabilities.
Compliance Recording
Microsoft Teams supports policy-based compliance recording through certified third-party recording partners.
Unlike a convenience recording initiated by a meeting participant, compliance recording is configured administratively and can capture required calls, meetings, and supported events under organizational policies.
The partner solution provides the recording infrastructure and related compliance functionality.
Financial institutions may use this model when recording specific communications is required for supervision or retention.
However, Teams compliance recording has documented exclusions.
According to Microsoft’s compliance recording documentation, it is not supported for E911 emergency calling, users operating in Survivable Branch Appliance mode, or PSTN calls for users in India.
Recording behavior also differs between ordinary user calls, call queues, and certain large meeting configurations.
For example, an organization using Survivable Branch Appliance functionality to maintain limited PSTN calling during a Microsoft cloud connectivity outage should not assume those calls will continue to be captured by its normal Teams compliance recording solution.
Similarly, a financial institution with operations in India must account for the documented PSTN recording limitation.
An enterprise should verify the recording coverage of all regulated call types, including internal and external calls, supported devices, call queues, conferencing scenarios, and contingency modes.
Where recording is mandatory, unsupported scenarios require an approved alternative workflow or compensating control.
Data Loss Prevention
Microsoft Purview DLP can evaluate sensitive information in supported Teams messages and Microsoft 365 files.
An enterprise may use policies to prevent the sharing of identified customer information or confidential documents through unauthorized channels.
The available protection depends on licensing and the particular communication workflow.
Identity and Administrative Controls
Teams integrates with Microsoft Entra ID for identity management, conditional access, and multi-factor authentication.
Organizations can manage access based on user identity, device conditions, and supported security policies.
Microsoft also provides administrative reporting and audit capabilities through the wider Microsoft 365 ecosystem.
Healthcare, Finance, and Government Considerations
Microsoft offers enterprise and government-specific Microsoft 365 environments, but these should not be treated as interchangeable.
A healthcare organization should verify contractual requirements for protected health information. A financial institution should validate compliance recording and retention across all relevant communication channels.
Government buyers must confirm the suitability of the specific Microsoft cloud environment rather than assuming that every commercial Teams feature is available in the required government environment.
Strengths: Deep productivity integration, extensive policy controls, Purview retention and eDiscovery, flexible telephony connectivity, and third-party compliance recording.
Limitations: Compliance functionality is distributed across Microsoft products, licenses, storage locations, and partner integrations. Teams compliance recording excludes E911, Survivable Branch Appliance mode, and PSTN calls for users in India, requiring additional planning for regulated operations.
Best use case: A regulated enterprise already using Microsoft 365 that wants unified calling and collaboration with established compliance administration and verified recording coverage.
2. Cisco Webex
Best for: Government agencies and large enterprises requiring secure calling, messaging, meetings, and access to government-specific cloud offerings.
Cisco Webex combines enterprise collaboration with business calling and administrative controls.
Its regulated-industry relevance is particularly strong in environments that require formal certification of cloud communication services.
Webex Calling and Enterprise Telephony
Webex Calling provides cloud business telephony with enterprise call management, routing, voicemail, and administrative functionality.
Organizations can use supported desk phones, mobile devices, and desktop clients.
Cisco also offers calling architectures and integrations that support organizations transitioning from existing Cisco voice infrastructure.
Meetings, Messaging, and File Sharing
Webex provides video meetings, direct and group messaging, file sharing, and collaboration features through its application environment.
Employees can move between calling, messaging, and meetings while administrators manage supported organizational policies.
Webex for Government
Cisco offers a dedicated Webex for Government suite.
The offering includes government-oriented meetings, messaging, calling, and related collaboration capabilities within a certified cloud service environment.
The FedRAMP Marketplace lists Webex for Government as a certified cloud service offering.
Procurement teams must still verify the current certification status, class, covered services, and applicable boundary.
Commercial Webex and Webex for Government should not be assumed to have identical features or integrations.
A government agency should also review whether required calling, recording, identity integrations, and administrative functions are available within the exact service offering.
Identity and Administrative Management
Cisco Control Hub provides administrative functions for managing users, supported devices, services, and security settings.
Organizations can integrate compatible identity systems and manage relevant collaboration policies.
Control Hub supports consistent administration across offices and departments.
Recording and Compliance Workflows
Webex offers recording capabilities and administrative settings for supported meetings and calls.
Organizations with formal recording or archiving obligations should assess the relevant recording services and available integrations separately.
A recorded meeting is not automatically equivalent to an immutable archive or a complete supervisory review system.
Hybrid and Existing Infrastructure Considerations
Cisco’s wider unified communications portfolio includes on-premises and hybrid options.
This can be relevant to enterprises migrating gradually from traditional telephony to cloud calling.
Hybrid designs still require a map of cloud-processed data.
Strengths: Enterprise calling, integrated collaboration, established administration, government-specific offerings, and support for complex communication environments.
Limitations: Features and certifications differ by service offering. Government procurement requires verification of the relevant FedRAMP certification boundary.
Best use case: A public-sector organization or regulated enterprise that needs mature cloud communications and a dedicated government service option.
3. Zoom Workplace and Zoom Phone

Best for: Healthcare providers, government agencies, and distributed enterprises seeking integrated calling, meetings, messaging, and documented security safeguards.
Zoom Workplace combines meetings, messaging, documents, and collaboration features. Zoom Phone adds business calling and enterprise telephony.
For regulated organizations, Zoom’s healthcare-related offerings and dedicated Zoom for Government environment are important distinctions.
Zoom Phone for Business Calling
Zoom Phone provides cloud telephony with call routing, voicemail, auto attendants, and supported call recording functionality.
Employees can make and receive business calls through desktop applications, mobile devices, and compatible telephone equipment.
Zoom also offers administrative functionality for managing calling policies and different business locations.
Zoom for Healthcare
Zoom provides healthcare-focused communication offerings that integrate meetings, calling, messaging, and related workflows.
The company supports Business Associate Agreements for eligible customers who need contractual safeguards relevant to HIPAA.
Zoom also provides healthcare-specific documentation and assurance reports related to its security controls.
However, the presence of a BAA does not mean every Zoom feature, integration, or AI workflow is automatically appropriate for handling protected health information.
Zoom for Government
Zoom for Government is a dedicated cloud communication offering designed for U.S. federal agencies and organizations working within government-specific security requirements.
It operates separately from the standard commercial Zoom environment and provides collaboration services within a specialized government cloud architecture.
The official FedRAMP Marketplace lists Zoom for Government with the following certification characteristics. Procurement teams should verify the current certification path and other procurement-specific fields directly in the Marketplace:
|
Certification attribute |
Zoom for Government |
|---|---|
|
FedRAMP status |
FedRAMP Certified |
|
Certification framework |
Revision 5 |
|
Certification class |
Class C (Moderate) |
|
Lifecycle phase |
Ongoing Certification |
|
Marketplace package ID |
FR1825941347A |
The certification applies to the defined Zoom for Government cloud service offering, not automatically to every commercial Zoom product. Buyers should consult the current Marketplace entry for any additional procurement-specific fields.
Government-Specific Calling and Collaboration
The FedRAMP Marketplace identifies multiple Zoom for Government services within the certified offering, including Zoom Meetings, Zoom Team Chat, Zoom Phone, Zoom Rooms, Zoom Whiteboard, and Zoom Contact Center.
The current listing also includes additional services such as Zoom Events, Zoom Hub, Zoom Node, Zoom Virtual Agent, and supported AI capabilities.
A government buyer can assess calling, messaging, meetings, and contact center services within one listed offering, while still confirming each product is available in its tenant.
Being in the certified boundary does not guarantee availability in every tenant. Agencies should verify licensing, integrations, and their own approval requirements.
Government Data Processing and Administration
Zoom describes its government environment as a dedicated U.S.-based communication infrastructure operated under government-specific security requirements.
Its government documentation addresses domestic data processing, controlled operational access, and infrastructure designed for federal use.
Certification and U.S. hosting do not replace agency-specific reviews.
An agency should determine where meeting recordings, transcripts, voicemail, messages, AI-generated outputs, and operational metadata are processed.
AI Companion for Zoom for Government
The FedRAMP Marketplace includes AI Companion for Zoom for Government within the listed service offering.
However, inclusion within a certified cloud service boundary does not mean that every AI feature is automatically approved for all sensitive information.
Administrators should review data handling, feature availability, access policies, and the agency’s rules concerning AI use.
For example, an agency may permit AI-generated summaries of routine administrative meetings while prohibiting their use for conversations containing particular categories of sensitive information.
Zoom for Government vs. Commercial Zoom
Commercial Zoom and Zoom for Government serve different procurement and security requirements.
|
Criterion |
Commercial Zoom |
Zoom for Government |
|---|---|---|
|
Primary audience |
Businesses, education, healthcare, general organizations |
U.S. government agencies and eligible partners |
|
Infrastructure |
Commercial Zoom service environment |
Dedicated government cloud environment |
|
FedRAMP certification |
Depends on the exact commercial service |
Dedicated certified offering |
|
Calling |
Zoom Phone with applicable licensing |
Zoom Phone listed within the government offering |
|
Messaging |
Zoom Team Chat |
Zoom Team Chat within the government offering |
|
AI capabilities |
Commercially available features subject to plan |
Government-specific AI capabilities subject to scope and approval |
|
Procurement |
Standard commercial channels |
Government-oriented procurement arrangements |
Feature parity should not be assumed. Government service availability and integrations may differ from the commercial product.
The same integration or AI setting may not be available in both environments.
Meeting Archiving
Zoom supports meeting and webinar archiving through compatible third-party archiving solutions.
Supported workflows can capture communication content such as video, audio, screen sharing, meeting chats, and metadata.
However, government and commercial archiving integrations should be evaluated separately. An integration available in commercial Zoom is not necessarily supported within Zoom for Government.
Administrative Security Controls
Zoom provides controls for meeting access, participant management, authentication, and selected content-sharing activities.
Organizations can establish policies governing recordings, meeting participation, and other relevant functions.
Healthcare Workflow Integration
Zoom supports integrations intended to connect communication systems with healthcare applications and electronic health record workflows.
Clinical integrations need their own data handling and contract assessment.
Strengths: Integrated communication tools, healthcare BAA support, meeting archiving integrations, administrative controls, dedicated Zoom for Government infrastructure, FedRAMP Class C certification, and government-specific calling and collaboration services.
Limitations: Healthcare suitability depends on contracts, configuration, integrations, and AI feature eligibility. Commercial and government environments have different service boundaries, and certified service inclusion does not establish unrestricted feature availability.
Best use case: A healthcare provider seeking integrated cloud communications or a government agency requiring a dedicated certified communication environment with meetings, messaging, and business calling.
4. RingCentral RingEX
Best for: Financial services and multi-location enterprises needing integrated business communication with recording, retention, and archiving options.
RingCentral RingEX combines cloud business telephony, messaging, meetings, and collaboration functions.
Its main regulated-use differentiator is integration with archiving and supervision systems.
Cloud Calling and Communication Management
RingCentral supports business calling, call routing, voicemail, messaging, and related communication workflows.
Employees can use supported desk phones, desktop applications, and mobile devices.
Multi-site administration helps organizations coordinate communication services across departments and locations.
Security Assurance and Product Scope
RingCentral publishes security and compliance information through its Trust Center, including SOC reports and product-specific assurance materials.
For example, RingCentral’s Trust Center lists a SOC 2 report with additional FINRA and HIPAA-related elements under RingCX, its contact center offering. That listing should not automatically be interpreted as confirmation that the same report covers every RingEX service.
Separately, RingCentral has published HIPAA-related assurance information addressing RingEX and RingCX, including references to audits of controls mapped to relevant HIPAA Security Rule requirements.
Regulated organizations should request the current reports covering the exact RingEX services, integrations, and deployment scope they intend to use.
A firm relying on a FINRA-related report should identify its named services and audit period.
A SOC 2 audit, even with additional criteria, does not itself certify a customer’s entire communication workflow as compliant with financial recordkeeping rules.
Communication Archiving
RingCentral provides archiving and export capabilities for supported communication content.
RingCentral Archiver supports exporting selected content to compatible external storage destinations.
The platform also provides message export APIs for supported message store information.
These functions can support records management, but exporting content does not automatically establish that an organization’s preservation, supervision, or legal hold obligations have been satisfied.
Compliance Integrations
RingCentral offers compliance-related integrations, including capabilities associated with Theta Lake.
Depending on the selected service and licensing, these integrations can support communication capture, archiving, surveillance, DLP-related workflows, eDiscovery, and legal hold.
For financial institutions, this is important because communication supervision often requires more than basic call recording.
A firm may need to preserve messages and recordings, search records, review flagged interactions, and maintain evidence for regulatory examinations.
Retention Considerations
RingCentral documentation identifies specific retention settings for different communication categories and account configurations.
Some content types and HIPAA-enabled account settings may have different retention behavior.
Organizations should not assume that the application automatically stores every message for the full period required by their regulator.
Retention settings, exports, and the archive of record should be tested as a single workflow.
Administrative Auditability
RingCentral provides audit trail functionality for selected administrative and privileged user activities.
This helps organizations review configuration changes and investigate access-related events.
Strengths: Enterprise communication features, published assurance materials, retention capabilities, messaging exports, and compliance integration options.
Limitations: Audit and certification documents have specific product boundaries. Advanced archiving and supervision may require third-party products, while retention behavior differs between content types and account configurations.
Best use case: A financial services organization seeking UCaaS with a documented path to communication archiving and supervisory review.
5. 8×8 Work

Best for: Regulated organizations that prioritize cloud telephony, integrated collaboration, multi-site management, and established security assurance.
8×8 Work combines business phone services, video meetings, messaging, and collaboration in a cloud-based platform.
Its broader portfolio also includes contact center services and communication APIs.
Enterprise Cloud PBX
8×8 provides cloud telephony features such as auto attendants, voicemail, call routing, ring groups, and call queues.
The platform also supports selected call recording and analytics capabilities.
Integrated Messaging and Video
8×8 Work brings voice, video meetings, team chat, and related communication functions into a unified application.
Employees can transition between communication modes without switching between unrelated systems.
Security Certifications and Compliance
8×8 publishes security assurance information through its Trust Center.
Available materials address frameworks and assessments such as ISO 27001, SOC 2, and applicable industry requirements.
8×8 also publishes healthcare-related compliance information and provides Business Associate Agreements for relevant customer arrangements.
The exact service scope and applicable contract must be verified before processing regulated information.
Healthcare Configuration
8×8 documentation provides specific recommendations for certain healthcare-sensitive workflows.
For example, its voicemail administration guidance recommends notification-only delivery instead of attaching voicemail audio to emails in situations where inappropriate forwarding could expose protected information.
A healthcare deployment should therefore verify voicemail notification settings as well as account-level safeguards.
Microsoft Teams Integration
8×8 offers telephony integration options for Microsoft Teams, including relevant connectivity models.
Its portfolio also identifies compliance recording through a certified technology partner for supported Teams environments.
These options can be useful for organizations that want to keep Microsoft Teams as their collaboration interface while using 8×8 telephony capabilities.
The deployment test should establish which provider captures, stores, and retains each record.
Recording and Retention Validation
Organizations using 8×8 for regulated calls should demonstrate that required call categories are recorded, exported to the designated archive where applicable, and retrievable after employee accounts change or are deactivated. Tests should distinguish 8×8 Work from separate contact center and partner recording products, since each may have different capture and retention behavior.
Analytics and Contact Center Integration
8×8 provides communication analytics and related contact center capabilities.
However, analytics and AI features should be assessed according to the data categories being processed.
Strengths: Integrated phone, meetings, and messaging; enterprise telephony; published security assurance; healthcare-related guidance; and Microsoft Teams connectivity.
Limitations: The compliance scope of 8×8 Work, contact center products, communication APIs, and partner recording solutions may differ.
Best use case: A multi-location healthcare or professional services organization seeking integrated cloud telephony and collaboration.
6. TrueConf Server

Best for: Government institutions, industrial organizations, regulated enterprises, and other environments that require privately managed communications or operation without public internet access.
TrueConf Server is an on-premises communication platform that combines video conferencing, corporate messaging, group chats, channels, and file sharing.
It is not conventional cloud UCaaS because the organization deploys and operates its own communication infrastructure. However, it addresses a significant part of the same unified communications requirement.
On-Premises Infrastructure Control
TrueConf Server can be deployed on customer-controlled Windows or Linux infrastructure.
The organization manages the server environment, network configuration, access policies, and supporting systems.
For regulated organizations, this can simplify certain data location and infrastructure control requirements by keeping communication services inside an approved environment.
The customer remains responsible for appropriate security controls and legal compliance.
Offline and Isolated-Network Communication
The full licensed version of TrueConf Server supports autonomous operation inside a corporate network without requiring continuous public internet connectivity.
Organizations can deploy the platform within LAN, VPN, or appropriately configured isolated network environments.
This is particularly relevant to critical infrastructure, industrial facilities, research institutions, and public-sector organizations that restrict external network access.
For example, a manufacturing facility may need operational video meetings and internal messaging to remain available even when the site is disconnected from external networks.
A conventional cloud UCaaS platform would normally require access to its provider infrastructure. TrueConf can support internal communication using locally available systems.
Corporate Messaging and File Sharing
TrueConf includes personal and group chats, channels, and file exchange.
Employees can coordinate work through internal communication services hosted by the organization.
ICAP-Based DLP Integration
TrueConf Enterprise supports integration with external Data Loss Prevention systems through the Internet Content Adaptation Protocol.
The integration allows supported chat messages and files to be checked by a compatible external DLP system before ordinary delivery.
Administrators can configure inspection behavior and the response to unwanted content.
For example, a research organization may use DLP policies to identify restricted documents or confidential customer information in supported conversations.
The connected DLP engine performs the inspection. TrueConf provides the communication platform and integration point.
This integration requires appropriate TrueConf Enterprise capabilities and a separate DLP engine.
Identity and Access Management
TrueConf Server supports integration with Active Directory and LDAP.
This enables organizations to administer accounts through existing identity infrastructure.
Organizations can also configure relevant administrative controls around their communication environment.
Enterprise Video Conferencing
TrueConf supports video conferencing for up to 2,000 participants, depending on licensing and configuration.
It also provides screen sharing, presentations, conference management, and support for compatible SIP and H.323 video conferencing equipment.
Federation Between Organizations
TrueConf supports federation between separately administered servers in compatible configurations.
Federation links organizations without requiring shared infrastructure ownership.
For example, two institutions may need to collaborate without transferring ownership or administration of their communication systems to a common cloud provider.
Federation should be configured with explicit trust, network, and security policies.
Recording and Information Governance
TrueConf supports conference recording and other communication administration functions.
However, recording functionality is not automatically equivalent to a regulated archive of record with all required retention, supervision, and legal hold capabilities.
Financial institutions or other organizations with formal recordkeeping obligations should verify the supported recording lifecycle and integration options against their exact requirements.
Government and Regulatory Suitability
TrueConf’s principal distinction for government and regulated organizations is its customer-controlled deployment model.
The platform can be installed within infrastructure operated and administered by the organization, including suitable isolated network environments.
This does not establish that the product holds every certification or authorization required by a particular government procurement program.
Regulatory suitability must be assessed separately according to the product edition, deployment architecture, applicable jurisdiction, and organization’s security requirements.
Organizations should evaluate the server environment, identity controls, encryption, logging, recording procedures, and required evidence of compliance.
Practical Application in a Regulated Environment
Consider a research organization operating a restricted internal network.
Employees need video meetings, group messaging, file exchange, and access to existing conferencing equipment.
Public cloud services are not permitted on the relevant network segment.
The organization deploys TrueConf Server on its own infrastructure and connects users through its internal identity systems.
For supported messaging workflows, it can also integrate a compatible DLP system through ICAP in TrueConf Enterprise.
This allows the organization to provide internal communications without depending on public internet connectivity for ordinary operation.
The organization remains responsible for maintenance, backups, access control, and retention.
Strengths: Customer-controlled deployment, isolated-network operation, enterprise video conferencing, corporate messaging, directory integration, SIP/H.323 interoperability, federation, and optional ICAP DLP integration.
Limitations: Not a conventional managed cloud UCaaS subscription. Infrastructure, maintenance, and regulatory controls require customer or managed-service administration. PSTN services and regulated archiving requirements must be evaluated separately.
Best use case: An organization that requires unified communications inside approved private infrastructure or an isolated network.
Boost your team’s productivity with TrueConf Server Free!
7. Dialpad Connect
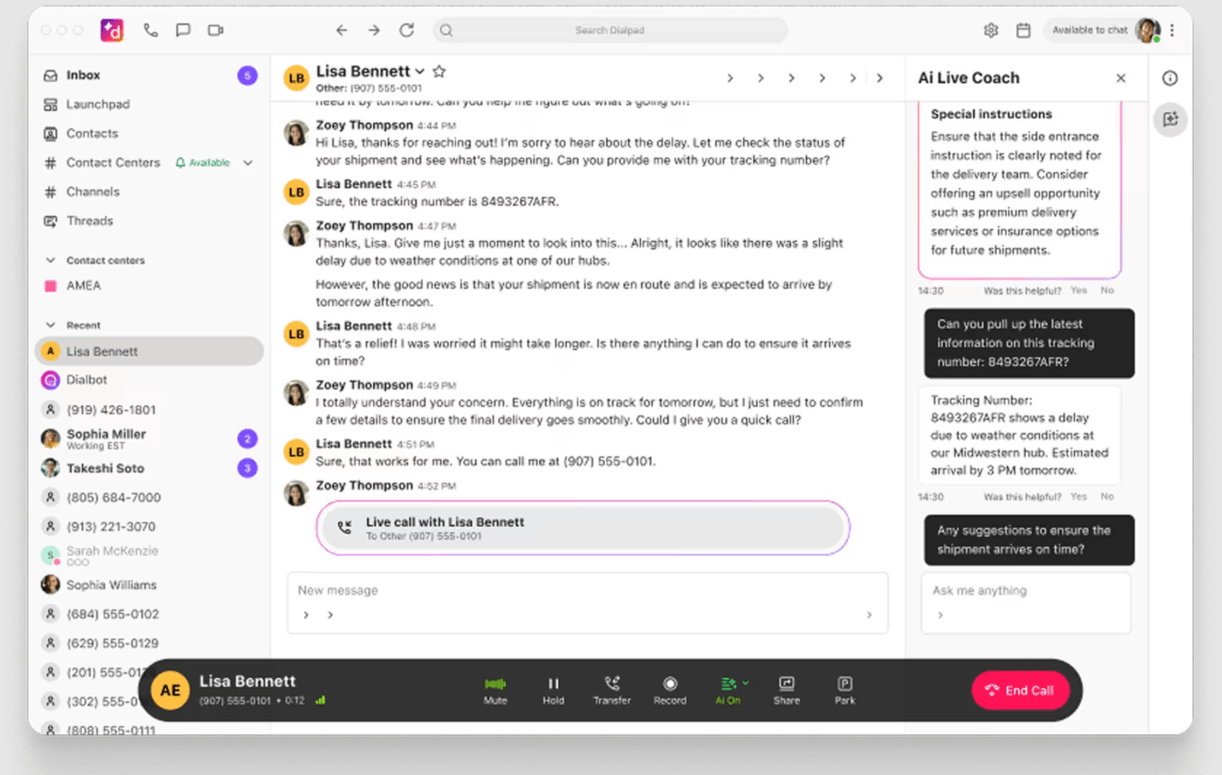
Best for: Healthcare and professional services organizations interested in cloud calling, messaging, and AI-assisted communication workflows.
Dialpad provides cloud business communication services with calling, messaging, meetings, and AI-related productivity capabilities.
Business Calling and Messaging
Dialpad Connect supports business telephony with administrative controls for calling, voicemail, and communication workflows.
Employees can communicate across supported desktop and mobile applications.
Dialpad also provides messaging and collaboration capabilities to support coordination beyond traditional calls.
AI-Assisted Communication
Dialpad emphasizes AI functionality across its communication and customer interaction products.
Relevant capabilities may include transcription, summaries, and conversation-related insights, depending on the selected service.
For example, a healthcare organization may permit AI-generated summaries of ordinary staff meetings while restricting AI processing of conversations containing sensitive patient information.
The organization should determine which AI settings are available to administrators and whether processing can be restricted for particular users or communication workflows.
Healthcare Business Associate Agreements
Dialpad allows company administrators on paid accounts to accept a Business Associate Agreement through the administration portal. Dialpad Meetings has a separate BAA acceptance workflow, and eligibility for that product should be checked against the relevant plan.
Its administrator documentation describes a process for reviewing and accepting a BAA through the administration portal.
The BAA governs a defined relationship, not every possible configuration.
A BAA should be reviewed together with the provider’s data handling terms, security controls, and the services actually used.
The organization should also verify whether AI-generated transcripts, summaries, recordings, and other derived content are covered by the applicable arrangements.
Administrative Management
Dialpad provides enterprise administration for users, offices, and supported calling settings.
Organizations can manage communication availability and account configuration across locations.
The exact identity integrations and policy options depend on the selected plans and capabilities.
Regulated organizations should confirm whether their proposed subscription supports the identity controls, administrative restrictions, and logging they require.
AI Feature and Contract Verification
A practical evaluation should use representative, non-sensitive test calls to check which transcripts, summaries, and analytics are generated, how administrators can disable or limit those functions, and what occurs when a user changes roles. The customer should map the resulting records against its BAA or other data processing agreement, rather than assuming that all features have identical contractual coverage.
Compliance Recording Considerations
Regulated financial institutions should not assume that ordinary call recording or AI transcripts meet all supervisory retention requirements.
They must verify recording capture, archive integration, retention controls, and legal hold support for the proposed deployment.
Strengths: Integrated cloud calling and messaging, AI-assisted workflows, centralized administration, and documented healthcare BAA availability.
Limitations: AI features require careful data governance. Formal recording and supervision requirements need validation against specific product capabilities, plans, and integrations.
Best use case: A healthcare or professional services organization that wants modern cloud communications with configurable AI features.
8. Vonage Business Communications
Best for: Regulated businesses seeking flexible cloud calling, messaging, video collaboration, centralized access controls, and configurable communication recording.
Vonage Business Communications provides cloud telephony and collaboration capabilities for organizations replacing traditional phone systems.
Its platform also connects with a broader ecosystem of communication APIs and business applications.
For regulated organizations, its administrative controls and recording configuration options deserve closer consideration than the general calling features alone.
Business Telephony and Call Routing
Vonage supports business calling functions such as call routing, voicemail, and administrative management.
Organizations can manage extensions, assign users to groups, configure telephone settings, and administer communication services across multiple locations.
For example, an insurance organization may need to route customer calls between regional offices while maintaining centrally managed user accounts.
The calling environment should be configured so that employees receive only the access necessary for their responsibilities.
Identity and Authentication Controls
The Vonage Business Communications administration environment provides security settings for supported users.
These include Single Sign-On, which allows employees to authenticate through a compatible organizational identity provider.
The platform also supports two-factor authentication for additional account protection.
Administrators can manage user types, relevant account settings, and access to supported web and mobile services.
Periodic administrative access reviews should address role changes and departed employees.
Centralized Call Recording
Vonage Business Communications provides company-level call recording capabilities.
Administrators can configure recording rules according to factors such as call direction, telephone number, and user extension.
For example, a company may establish a rule requiring selected customer service lines to be recorded while excluding internal administrative extensions that do not require the same treatment.
Recordings can be managed through the administration environment, with supported playback, download, and related management functions.
These features support quality assurance and dispute resolution, but do not by themselves constitute a regulated archive of record.
A financial institution that must preserve specific communications should verify capture coverage, retention controls, access restrictions, and the availability of any required external archive or supervisory process.
On-Demand Recording
Vonage also supports on-demand recording in relevant configurations.
This allows authorized users to initiate recording for selected conversations rather than capturing every call automatically.
This can suit selective documentation, but user-initiated recording cannot substitute for mandatory policy-controlled capture.
Recording Access and Administrative Permissions
Vonage provides different administrative user types and recording management permissions.
Its administration documentation distinguishes access to recordings based on the user’s role and assignment.
For example, administrators may be restricted from viewing recordings associated with extensions for which they lack the required authorization.
Recording access should still be reviewed alongside download permissions, sharing functionality, retention requirements, and the ability to delete content.
Partner and Guest Administrative Access
Vonage Business Communications includes a controlled partner guest access process for supported implementation and support relationships.
Certified partners can request temporary or ongoing access through the appropriate administrative workflow, subject to customer approval.
The documented guest access model excludes sensitive administrative areas such as call recording, phone number transfers, Single Sign-On, user provisioning through SCIM, and security settings.
A support provider may need access to selected configuration functions without receiving unrestricted control over identity settings or sensitive recordings.
Organizations should still maintain a formal process for reviewing, approving, and removing partner access.
Business Application Integrations
Vonage supports integrations intended to connect communication activities with business software.
For example, customer-facing employees may benefit from accessing relevant customer information during calls or maintaining communication context in CRM records.
In regulated environments, integrations must be evaluated for permissions, data minimization, and the handling of customer records.
The organization should map which integrated systems receive call metadata or recordings and establish access and retention rules for each.
Healthcare and Assurance Considerations
Vonage publishes information about security and compliance capabilities relevant to healthcare, payment processing, and enterprise communication.
Its unified communications offerings have historically undergone relevant security and HITRUST-related certification processes.
Regulated buyers should request current assurance materials rather than rely on historical certifications or broad compliance statements.
The exact product, certification period, contractual commitments, and service boundary must be verified before procurement.
Practical Application
Consider an insurance company with multiple regional offices.
The organization uses Vonage Business Communications to manage business calling, configure extensions, and route customer inquiries.
Employees authenticate through supported organizational identity controls, and selected departments use centrally configured call recording rules.
The administration team restricts recording access according to employee responsibilities.
When an external implementation partner requires temporary administrative access, the company uses a controlled approval process rather than sharing unrestricted administrator credentials.
The firm must still test its required retention and supervisory processes.
Strengths: Cloud telephony, centralized administration, Single Sign-On, two-factor authentication, configurable company recording, on-demand recording, role-based recording access, controlled partner access, and business application integrations.
Limitations: Recording functionality and security controls depend on the selected service and configuration. Standard call recording does not automatically satisfy formal financial supervision, immutable retention, or legal hold requirements.
Best use case: A regulated professional services, insurance, or healthcare organization seeking centrally managed calling with configurable identity and recording controls.
9. GoTo Connect
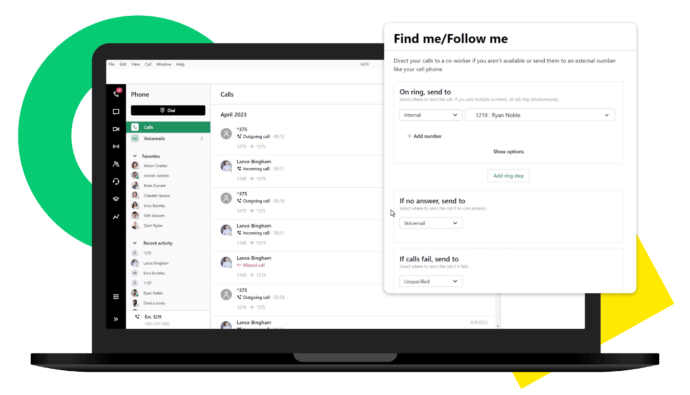
Best for: Multi-site healthcare providers, professional services firms, and organizations seeking integrated cloud telephony with communication management features.
GoTo Connect combines a cloud phone system with video meetings, messaging, and administrative tools.
Cloud Phone System
GoTo Connect provides features such as auto attendants, call queues, configurable dial plans, voicemail, and call routing.
For example, a healthcare provider can route patient calls to the appropriate department while maintaining a consistent organization-wide phone system.
Meetings and Messaging
The platform includes video meetings, team messaging, and file sharing.
GoTo also offers supported meeting recording and AI-assisted features.
Healthcare Compliance Guidance
GoTo publishes healthcare-related guidance explaining how its safeguards and customer configuration responsibilities contribute to HIPAA-related use cases.
The guidance addresses issues such as access controls, encryption, audit logging, and the protection of stored communication content.
GoTo publishes a Business Associate Addendum for applicable services, including GoTo Connect. Healthcare customers should verify that their agreement covers the specific services and data flows they intend to use.
Healthcare organizations should review the contract, service scope, and configuration guidance before using the platform to process protected health information.
Administrative and Audit Controls
GoTo Connect provides administrative tools for managing users, communication settings, and calling workflows.
Its broader security documentation addresses access controls and audit-related safeguards.
Recording and AI Governance
GoTo offers call and meeting recording capabilities as well as AI-related functionality.
Organizations must define who may record communications, where recordings are retained, and whether generated transcripts or summaries contain regulated information.
For finance or legal use cases requiring formal preservation, the availability of an appropriate archive and supervisory process should be validated.
Administrators should test whether recordings are captured consistently across the required users, call types, and devices.
If the organization needs mandatory recording, ordinary user-controlled recording should not be treated as equivalent to an enforced compliance recording solution.
Healthcare Deployment Scenario
A clinic group could pilot GoTo Connect across two locations, testing how reception staff route patient inquiries, whether voicemail notifications expose protected information, and who may play back recordings. The trial should document call routing during internet disruptions and confirm that any AI-generated transcripts are restricted to the authorized workflow. This is a deployment test plan, not a claim that GoTo automatically meets HIPAA obligations.
Multi-Site Operations and Continuity
GoTo Connect can help organizations coordinate calling across multiple locations.
The continuity plan should test provider outages, network interruptions, and emergency calling.
Strengths: Cloud PBX features, call routing, meetings, messaging, centralized administration, healthcare guidance, and communication workflow tools.
Limitations: Regulated recording and retention workflows need specific verification. AI features and integrations may introduce additional data governance requirements.
Best use case: A healthcare or professional services organization seeking an integrated cloud phone and collaboration system.
UCaaS Providers Compared by Regulatory Requirements
The following comparison separates documented features and offerings from capabilities that require further verification.
|
Provider |
Healthcare arrangements |
Financial recording and archiving |
Government offering |
Infrastructure control |
|---|---|---|---|---|
|
Microsoft Teams Phone |
Documented enterprise contractual arrangements; scope must be verified |
Third-party compliance recording and Purview retention |
Dedicated government cloud offerings |
Provider-managed cloud with telephony integration options |
|
Cisco Webex |
Enterprise security controls; healthcare contract scope requires verification |
Recording capabilities and supported integrations; coverage must be tested |
Webex for Government, FedRAMP-certified offering |
Cloud, with broader Cisco hybrid options |
|
Zoom |
Documented BAA arrangements for eligible healthcare customers |
Meeting archiving integrations; required capture coverage needs verification |
Zoom for Government, FedRAMP Class C (Moderate) certified |
Provider-managed commercial and dedicated government environments |
|
RingCentral RingEX |
Documented RingEX healthcare assurance and BAA arrangements |
Archiver, exports, and third-party compliance integrations |
Government-specific eligibility not established in this comparison |
Provider-managed cloud |
|
8×8 Work |
Documented healthcare guidance and applicable BAA arrangements |
Recording and partner-based options; supervisory suitability requires verification |
Government-specific certification not established in this comparison |
Provider-managed cloud |
|
TrueConf Server |
Customer-controlled environment; compliance requires separate assessment |
Recording supported; regulated archive-of-record capability requires verification |
Customer-controlled on-premises deployment; regulatory suitability requires separate assessment |
On-premises and suitable isolated networks |
|
Dialpad Connect |
Documented BAA availability for eligible paid accounts |
Recording and archive-of-record suitability requires verification |
Government-specific certification not established in this comparison |
Provider-managed cloud |
|
Vonage Business Communications |
Published healthcare assurance information; current scope requires verification |
Configurable recording; regulated retention and supervision require separate assessment |
Government-specific certification not established in this comparison |
Provider-managed cloud |
|
GoTo Connect |
Documented healthcare guidance and BAA arrangements where applicable |
Recording available; formal archiving requires verification |
Government-specific certification not established in this comparison |
Provider-managed cloud |
A documented feature is not evidence of customer compliance. Partner integrations require separate validation; an unverified status means this comparison does not establish whether the capability is available.
Insight 3. Compliance Recording Is Not the Same as Ordinary Meeting Recording
Many communication platforms allow users to record meetings and calls, but this does not automatically satisfy regulated recordkeeping obligations.
A user-controlled recording can depend on the participant remembering to start it. A regulated recording process may instead require administrators to enforce capture policies, preserve relevant communications, prevent unauthorized tampering, and support search or supervisory review.
For example, Microsoft Teams uses certified third-party solutions for policy-based compliance recording. Zoom supports compatible archiving integrations, while RingCentral offers relevant communication export and compliance options.
However, even a policy-based recording system may have unsupported scenarios. Microsoft Teams, for example, excludes certain emergency, survivability, and regional PSTN calling configurations from its compliance recording functionality.
A regulated organization should evaluate the complete record lifecycle: capture, storage, retention, access control, supervision, legal hold, retrieval, and deletion.
The required controls depend on the applicable regulation and the specific type of communication.
How to Choose a UCaaS Provider for a Regulated Organization?
Start with a requirements matrix and test each proposed service against realistic workflows.
1. Map Communication Data
Identify which communication channels carry sensitive or regulated information.
These may include telephone calls, voicemail, video meetings, instant messages, files, meeting transcripts, recordings, and AI-generated summaries.
Not every channel necessarily requires the same controls.
2. Define Regulatory Obligations
Work with compliance and legal teams to identify applicable requirements.
Determine whether the organization needs a BAA, formal communication retention, data processing agreements, government cloud certification, or specific operational resilience controls.
The result should be a requirements matrix that vendors can answer directly.
3. Verify Service-Specific Assurance
Request current security documentation covering the exact product.
Relevant materials may include SOC reports, ISO certifications, penetration testing summaries, contractual safeguards, and applicable government certification records.
For FedRAMP-related procurement, verify the certification class and service boundary in the current FedRAMP Marketplace.
Do not assume a vendor-wide compliance statement covers every purchased service.
4. Test Recording and Retention
A regulated financial institution should validate whether required communications are recorded automatically and preserved according to policy.
Tests should cover the actual users, devices, communication channels, and external participants involved.
They should also cover less common scenarios, including emergency calling, branch survivability modes, international PSTN calls, call queues, and supported external meeting configurations.
Not every platform supports compliance recording in all these cases. The evaluation should document which scenarios are excluded and how the organization will address them.
A retained compliance record should remain available for authorized review even when ordinary application content is edited or deleted, where the applicable records rules require such preservation.
5. Assess Data Location and Subprocessors
Determine where relevant content and metadata are processed.
Review the use of subprocessors, international transfers, administrative access, and contractual commitments.
Also consider backup copies and disaster recovery locations.
6. Evaluate Business Continuity
Assess provider availability, service dependencies, emergency calling, and alternative communication methods.
A continuity exercise should include a realistic provider outage and determine which operations remain available.
7. Test AI Governance
Review whether AI features can be disabled or restricted by user group.
Determine which information is processed, where outputs are stored, and whether transcripts or summaries introduce additional retention obligations.
The use of AI features within a certified government environment should be evaluated against the actual certification scope and agency-specific approval.
8. Define Exit and Migration Requirements
Regulated organizations may need to export communication records, migrate telephone numbers, preserve archives, and terminate services without losing required evidence.
These requirements should be addressed contractually before deployment.
UCaaS Vendor Evaluation Checklist
|
Evaluation criterion |
Questions for the provider |
Evidence to request |
|---|---|---|
|
Regulatory scope |
Which exact services support our obligations? |
Product-specific compliance documentation |
|
Data location |
Where are content, recordings, and metadata processed? |
Data flow and residency documentation |
|
Identity |
Can we enforce MFA, SSO, and role-based access? |
Administrative demonstration |
|
Recording |
Can required calls and meetings be captured automatically? |
Recording architecture and test results |
|
Recording exceptions |
Which call types, locations, and contingency modes are unsupported? |
Product limitations and test results |
|
Retention |
Can records be preserved for required periods? |
Retention and archive specifications |
|
eDiscovery |
Can authorized reviewers search and export records? |
Demonstration or integration documentation |
|
Encryption |
How is content protected in transit and at rest? |
Security architecture |
|
Government certification |
What is the current FedRAMP status, class, and certification boundary? |
Current FedRAMP Marketplace listing |
|
AI governance |
Can AI processing be restricted by workflow? |
AI data handling documentation |
|
Incident response |
What notification and support commitments apply? |
Contractual terms and incident procedures |
|
Continuity |
How are outages and critical failures handled? |
Service continuity documentation |
|
Emergency calling |
How are location and emergency calls supported? |
Region-specific emergency calling documentation |
|
Exit planning |
How are records and communication services migrated? |
Export and termination procedures |
A provider may demonstrate strong administrative controls but lack the precise retention integration required by a financial institution. Another may support appropriate healthcare contracts while offering features that must be disabled before handling protected information.
UCaaS Deployment Strategies for Healthcare, Finance, and Government
Choose the model according to operational priorities and data sensitivity.
|
Scenario |
Main priority |
Suitable approach |
|---|---|---|
|
Hospital with multiple clinics |
Secure patient communication and administrative calling |
Cloud UCaaS with appropriate BAA and healthcare configuration |
|
Investment firm |
Communication recording and supervision |
UCaaS with validated compliance recording and archive integration |
|
Government agency |
Certified cloud services and controlled access |
Appropriate government-specific cloud offering |
|
Research laboratory with restricted network |
Internal operation without public internet |
On-premises unified communications |
|
Insurance company |
Customer calling and secure internal collaboration |
Cloud UCaaS with identity, recording, and retention governance |
|
Industrial facility |
Continuity during external network disruptions |
Private communication environment or validated contingency architecture |
|
Multinational financial organization |
Regional obligations and third-party risk |
Governed cloud or hybrid communication strategy |
The same organization may use different communication models for different workloads. For example, a regulated enterprise might use cloud telephony for general administration while retaining a separate private communication environment for sensitive operational coordination.
A mixed architecture adds governance work but can separate restricted and routine operations.
Insight 4. Data Sovereignty and Data Residency Are Not the Same
A provider may offer data storage in a selected geographic region without giving the organization control over every aspect of data processing.
Administrative access, subprocessors, backups, metadata, and AI services can remain relevant even when primary storage is located in the required country.
Data residency describes where certain information is stored or processed. Data sovereignty concerns the broader legal and operational control applicable to that information.
For regulated communications, selecting a regional data center is only one part of assessing control over sensitive information.
Organizations should evaluate contractual access rights, technical dependencies, infrastructure administration, and the actual data flows.
Common Mistakes When Selecting UCaaS for Regulated Organizations
One frequent mistake is relying on broad claims such as secure, compliant, or enterprise-grade without asking which specific controls support the intended use case.
Another is treating ordinary meeting recordings as sufficient for formal records preservation. The organization may later discover that records are missing, stored under user-controlled permissions, or unavailable for appropriate supervision.
AI functionality can create a similar problem. A service may offer useful summaries and transcripts, but the organization needs to determine whether these outputs contain regulated information and how they are governed.
Government procurement can introduce another mistake: assuming that a vendor’s FedRAMP certification applies to every commercial product it offers. Certification applies to a defined cloud service boundary, and actual agency use may require separate authorization and configuration.
Some businesses also overlook emergency calling and operational continuity when replacing traditional telephone systems with cloud communication.
Finally, organizations may fail to plan for vendor exit. Exporting historical communication records and migrating telephony services can be difficult when requirements were not considered during procurement.
Measuring UCaaS Security and Compliance Effectiveness
Post-deployment governance should measure controls using evidence from actual communication workflows.
|
Metric |
What it demonstrates |
|---|---|
|
Required communication capture rate |
Whether designated calls or meetings are consistently captured |
|
Recording and archive failures |
Whether compliance records are lost or delayed |
|
Recording exclusion coverage |
Whether unsupported scenarios have documented alternatives |
|
Retention coverage |
Whether relevant content is governed by required policies |
|
Unauthorized access events |
Whether identity controls are operating effectively |
|
Privileged configuration changes |
Whether administrative activity is auditable |
|
Service availability |
Whether critical communication functions remain accessible |
|
Incident response performance |
Whether provider and customer processes meet expectations |
|
Unapproved communication usage |
Whether employees are using ungoverned channels |
|
Exit test completion |
Whether critical records and services can be migrated |
|
AI feature policy coverage |
Whether sensitive workflows are governed appropriately |
A healthcare organization may emphasize access control and protected information handling, while a financial services firm may prioritize communication capture, retention, and supervisory access.
Insight 5. The Best Regulated UCaaS Architecture May Use More Than One Communication Platform
Consolidating communication services can reduce administration costs and improve the user experience.
However, different business functions may have incompatible infrastructure requirements.
A financial services firm may need a cloud communication platform with extensive archiving integrations for customer-facing operations. The same organization may also operate a restricted research or security environment where cloud connectivity is prohibited.
Trying to force both workloads into one deployment model can create unnecessary compromises.
A carefully governed architecture may use different communication environments for different sensitivity levels, provided identity, access, retention, and operational responsibilities remain clearly defined.
The objective is not necessarily to standardize every conversation on one platform, but to ensure each communication workflow operates within an appropriate and verifiable control environment.
Conclusion
The best UCaaS providers for regulated organizations are those that combine reliable calling, video meetings, and messaging with the controls needed for each industry’s security and compliance obligations. Microsoft Teams Phone offers extensive Microsoft 365 governance and compliance recording integrations, Cisco Webex and Zoom provide dedicated FedRAMP-certified government offerings, and Zoom also supports healthcare workflows. RingCentral and 8×8 provide enterprise telephony with relevant assurance and integration capabilities, while Dialpad, Vonage, and GoTo Connect offer additional cloud communication options. TrueConf Server addresses organizations that need unified communications on privately controlled infrastructure or isolated networks.
Choosing the right platform requires more than reviewing compliance certifications or comparing subscription prices. Organizations should verify exact service boundaries, recording and retention requirements, contractual safeguards, data processing locations, AI governance, and business continuity arrangements. A structured proof of concept, supported by legal and security review, helps determine whether the proposed solution can meet real operational requirements without introducing unacceptable risks.
Empower your video conferencing experience with TrueConf!
FAQ
What are the best UCaaS providers for regulated organizations?
Microsoft Teams Phone, Cisco Webex, Zoom, RingCentral, and 8×8 are important cloud UCaaS options for regulated organizations. Their suitability depends on applicable regulations, required recording and retention controls, contractual safeguards, and deployment restrictions. Organizations that require on-premises or isolated-network communication may also evaluate TrueConf Server as an alternative to conventional UCaaS.
Can UCaaS be HIPAA compliant?
Yes, UCaaS can support HIPAA-regulated workflows when the appropriate contractual safeguards, technical controls, and operational practices are in place. Healthcare organizations should verify whether a Business Associate Agreement is required and which services it covers. A provider’s general security certification does not automatically make every feature or integration suitable for protected health information.
Which UCaaS providers are suitable for financial services?
Microsoft Teams Phone, RingCentral, Cisco Webex, and other enterprise communication platforms may support financial services through recording, archiving, or compliance integrations. The organization must verify that the selected configuration captures and preserves all communications required by its applicable rules. Ordinary call recording does not automatically satisfy financial supervision and books and records obligations.
Which UCaaS providers are FedRAMP certified?
Cisco Webex for Government and Zoom for Government are examples of dedicated government cloud communication offerings with FedRAMP certification. As of November 2026, the FedRAMP Marketplace lists Zoom for Government as a Revision 5, Class C (Moderate) certified service. Government agencies must verify the exact certification boundary, current status, covered services, and applicability to their intended deployment.
What is the difference between UCaaS and on-premises unified communications?
UCaaS is delivered primarily through provider-managed cloud infrastructure, while on-premises unified communications is deployed on infrastructure controlled by the organization. Cloud UCaaS can simplify maintenance and scaling, whereas on-premises systems can offer greater direct control over data location, network access, and operational dependencies. Neither model guarantees compliance without appropriate configuration and governance.
Can regulated organizations use AI features in UCaaS?
Yes, but AI features should be evaluated according to the information they process and the organization’s regulatory obligations. Administrators should verify how transcripts, summaries, and other outputs are stored, accessed, retained, and shared. Sensitive workflows may require restrictions or additional contractual and technical safeguards.
What should a regulated organization check before buying UCaaS?
The organization should evaluate service-specific compliance evidence, identity controls, encryption, communication recording, retention, eDiscovery, data residency, third-party dependencies, business continuity, and exit options. Government buyers should also verify current FedRAMP certification details, while financial organizations should test unsupported recording scenarios and plan appropriate alternatives. These requirements should be documented before vendor selection and tested against actual business workflows.
About the Author
Diana Shtapova is a product specialist and technology writer with three years of experience in the unified communications industry. At TrueConf, she leverages her deep product expertise to create clear and practical content on video conferencing platforms, collaboration tools, and enterprise communication solutions. With a strong background in product research and user-focused content development, Diana helps professionals and businesses understand core product features, adopt new technologies, and unlock the full potential of modern collaboration software.
Follow us on social networks