
Defense Communication Systems: 7 Layers From Radio to C2
A defense communication system is the communications architecture used to exchange voice, video, messages, files, location data, sensor feeds, and command information across military and defense environments. It can connect personnel, command posts, headquarters, vehicles, aircraft, ships, sensors, unmanned systems, and fixed installations.
A modern defense communication system is rarely one product. It normally combines tactical radios, MANET, satellite and terrestrial transport, secure IP networks, encryption, gateways, identity services, video and messaging applications, and command and control software. The architecture must remain usable when bandwidth falls, individual links fail, sites become disconnected, or access to public infrastructure is unavailable.
For system design, the objective is not to compare products by feature count alone. Communication layers should instead be evaluated according to their role, interoperability, security requirements, dependencies, and expected operating conditions.
|
Communication area |
Primary function |
Typical technologies |
|---|---|---|
|
Tactical voice |
Connect personnel, units, vehicles, and command elements |
HF, VHF, UHF, software defined radio |
|
Tactical data |
Exchange positions, messages, telemetry, and operational data |
MANET, tactical data links, IP networking |
|
Beyond line of sight connectivity |
Connect geographically separated units and facilities |
SATCOM, HF, terrestrial backhaul |
|
Video |
Support command conferences, remote coordination, and video distribution |
Secure video conferencing, RTP, H.264, H.265 |
|
Collaboration |
Exchange messages, files, voice, video, and shared information |
On-premises collaboration servers, secure messaging |
|
Command and control |
Deliver operational information to decision makers |
C2 and C4ISR applications |
|
Security |
Protect identities, data, and infrastructure |
Encryption, access control, segmentation, certificates |
|
Resilience |
Preserve communications after failures |
PACE, redundant transport, MANET, alternative links |
|
Interoperability |
Connect different systems and generations of equipment |
Gateways, SIP, H.323, RoIP, APIs, federation |
A useful high level model is:
Defense communication system = endpoints + transport + secure networking + communication applications + command applications + identity and security + management.
What Is a Defense Communication System?

A defense communication system is an integrated set of hardware, software, networks, and security controls designed to provide dependable information exchange for military or defense operations.
The category can include:
- tactical radios;
- satellite communications;
- mobile ad hoc networks;
- private IP networks;
- encrypted network devices;
- secure messaging;
- voice and video conferencing;
- file exchange;
- command and control software;
- mapping and situational awareness systems;
- sensor and video distribution;
- identity directories;
- gateways between legacy and modern systems;
- centralized network and device management.
Current NATO digital strategy documents describe a similar architectural direction, with emphasis on secure and interoperable digital capabilities, Zero Trust principles, federated environments, edge capabilities, diversified technical solutions, and communication resilience.
How Defense Communications Relate to C2 and C4ISR?
Defense communications provide the information transport and collaboration foundation used by command systems.
|
Term |
Meaning |
Relationship to communications |
|---|---|---|
|
C2 |
Command and Control |
Uses communications to distribute orders and operational information |
|
C3 |
Command, Control and Communications |
Explicitly adds communications to C2 |
|
C4 |
Command, Control, Communications and Computers |
Adds computing infrastructure and digital processing |
|
C4ISR |
Command, Control, Communications, Computers, Intelligence, Surveillance and Reconnaissance |
Combines communications with computing, intelligence, sensors, surveillance, and operational decision support |
A tactical radio is not a complete C4ISR system. Neither is a video conferencing server. Each can form one component of a broader information environment.
This distinction is important because products from different layers can address fundamentally different communication tasks.
What a Defense Communication System Looks Like in Practice?
At a conceptual level, a communication chain may connect:
user or sensor → tactical network → field or vehicle gateway → long distance transport → protected IP network → command environment → collaboration and C2 applications
The actual structure depends on the environment.
A headquarters network may not require a tactical MANET. A mobile unit may primarily rely on radio connectivity and local networking. A protected facility may use internal IP networks, conferencing, telephony, directories, and other locally hosted applications without public internet connectivity.
Insight 1: The communication chain is usually a more useful unit of analysis than an individual product. A system can have extensive functionality while still depending on an unavailable identity, transport, licensing, or processing service.
Why Defense Communication Systems Differ From Commercial Communications?

Commercial communications usually operate under relatively predictable network conditions. Users often have continuous access to internet connectivity, cloud services, identity providers, and vendor infrastructure.
Defense environments can impose different constraints.
A site can become isolated. Available bandwidth can change. Communication nodes can move. Different security domains may coexist. Some information may have to remain within organization controlled infrastructure.
A defense communication architecture therefore raises questions such as:
- What happens if the primary communication path becomes unavailable?
- Which functions remain available on constrained networks?
- Can users communicate without public internet access?
- Where are credentials, messages, recordings, and metadata stored?
- Can equipment from different generations and vendors interoperate?
- How are users, devices, and administrators authenticated?
- Can access be separated according to roles or information domains?
- Which functions depend on centralized services?
These questions can be more important than the total number of application features.
Core Layers of a Defense Communication System
The following model shows where major components sit within the architecture.
|
Layer |
Purpose |
Typical components |
|---|---|---|
|
1. Tactical edge |
Connect people, vehicles, sensors, and mobile platforms |
Tactical radios, rugged devices, MANET nodes |
|
2. Transport |
Carry traffic between users, sites, and networks |
SATCOM, HF, fiber, microwave, private LTE, 5G |
|
3. Secure networking |
Route and protect traffic |
Routers, firewalls, encryption devices, gateways, QoS |
|
4. Communication applications |
Support human communication |
Messaging, telephony, video conferencing, file sharing |
|
5. Command applications |
Organize operational information |
C2 platforms, mapping, common operating picture |
|
6. Identity and security |
Control access |
Directories, certificates, authentication, role controls |
|
7. Management |
Configure and monitor the environment |
Network management, logging, administration |
This layered model helps separate technologies by role before their individual functions are compared.
Defense Communication Systems in 2026: Current Statistics
Military communication infrastructure continues to receive investment in areas such as secure connectivity, SATCOM, battlefield networking, and digital command systems.
According to Fortune Business Insights, the global military communication market was estimated at USD 42.10 billion in 2025 and USD 44.80 billion in 2026. The same forecast estimates a market size of USD 70.20 billion by 2034, corresponding to a projected compound annual growth rate of 5.8 percent.
The analysis also estimates that:
- North America accounted for 38.90 percent of the market in 2025;
- hardware could represent 68.75 percent of the market in 2026;
- SATCOM could account for 40.89 percent of the technology segment in 2026;
- the United States military communication market could reach USD 12.97 billion in 2026.
These figures are market estimates, not measurements of operational effectiveness. They nevertheless illustrate continuing investment in connected platforms, communications infrastructure, secure data exchange, and integration between tactical networks and digital command systems.
Main Defense Communication Technologies and Their Roles
This section focuses on the function of each technology within the wider architecture.
Tactical radio communication
Tactical radios provide voice and data connectivity for personnel, vehicles, aircraft, and command elements.
Modern software defined radios can support multiple waveforms, frequency bands, security functions, and network capabilities. Depending on the implementation, they can also transport position information, video, sensor data, or IP traffic.
Mobile ad hoc networks
A mobile ad hoc network, or MANET, is a network in which participating nodes can establish and reorganize connectivity without relying on a conventional fixed base station.
MANET is relevant where personnel, vehicles, cameras, sensors, or unmanned platforms move and network topology changes.
MANET provides connectivity. Applications such as voice, video, mapping, messaging, or telemetry use that connectivity as a transport layer.
Satellite communications
Satellite communication provides beyond line of sight connectivity between geographically separated users and sites.
It can form part of the transport infrastructure connecting headquarters, remote facilities, vessels, aircraft, and field environments.
SATCOM itself does not provide the complete application, identity, security, and command architecture built on top of the connection.
HF communications
HF radio can provide long range communication without relying on satellite infrastructure.
It can therefore form one part of a diversified communications architecture where more than one transport mechanism is required.
Secure IP networks
IP infrastructure can transport voice, video, messaging, files, sensor information, command applications, and administrative traffic.
This convergence increases the importance of network segmentation, authentication, routing, traffic prioritization, monitoring, gateway security, and application availability.
Secure video conferencing and collaboration
Defense related organizations may also require video meetings, messaging, file exchange, screen sharing, and group communications.
Where external services are unsuitable for the deployment model, collaboration applications can be placed inside organization controlled infrastructure.
The applicability of a particular solution depends on the security requirements, information category, certification requirements, and regulatory environment of the organization operating it.
Command and control systems
C2 systems combine communication with operational information and decision support.
Such platforms can receive information from personnel, vehicles, sensors, maps, communications systems, or external applications and present that information within a common operational environment.
Communications transport information. C2 software processes or presents it for command functions.
Key Requirements for a Defense Communication System
|
Requirement |
Question to ask |
Why it matters? |
|---|---|---|
|
Availability |
What happens if the primary path disappears? |
One network failure should not automatically remove all communications |
|
Data control |
Where are messages, recordings, credentials, and metadata stored? |
Information may be subject to specific storage and access requirements |
|
Interoperability |
Which networks, endpoints, and protocols can connect? |
Existing environments are often heterogeneous |
|
Network independence |
Can critical functions operate without external services? |
Some systems operate in isolated networks |
|
Bandwidth tolerance |
Which features remain usable on constrained links? |
Some transport networks provide limited capacity |
|
Latency tolerance |
How does the application behave over delayed transport? |
Long distance links can introduce latency |
|
Security boundaries |
Can users and information domains be separated? |
Access requirements can differ between groups |
|
Administration |
Can users, devices, and policies be managed centrally? |
Complex deployments require controlled administration |
|
Scalability |
Can the architecture expand across additional users or sites? |
Infrastructure requirements may change over time |
|
Legacy integration |
Can existing telephony and video infrastructure remain connected? |
Full replacement is not always practical |
|
Update model |
Can software be maintained in isolated environments? |
Internet based update mechanisms may not always be available |
|
Logging |
Can administrators audit access and activity? |
Security processes require traceability |
Insight 2: Maximum throughput and communication resilience are different characteristics. An independent lower capacity communication path can remain useful when a higher capacity primary connection becomes unavailable.
PACE and Communication Resilience
PACE stands for Primary, Alternate, Contingency, Emergency.
It is a communications planning concept based on maintaining more than one method of communication for important processes.
At a high level, a system can distinguish between a preferred communication path and independent alternatives that remain available under different network conditions.
Current NATO digital strategy materials also refer to diversified technical solutions and PACE based approaches in the context of mission critical service resilience.
The important principle is dependency diversity.
Several applications that all depend on the same network, identity service, data center, or gateway do not necessarily provide independent resilience.
Insight 3: Redundancy should be evaluated at the dependency level. Two applications can still share the same single point of failure.
Defense Communication Security
Security cannot be evaluated solely by checking whether a product uses encryption.
A protected communication environment can involve:
- encrypted signaling;
- encrypted media;
- device authentication;
- user authentication;
- identity management;
- role based permissions;
- certificate management;
- network segmentation;
- administrator restrictions;
- endpoint protection;
- software integrity;
- controlled updates;
- logging and auditing;
- secure key management.
Current defense digital strategies increasingly reference Zero Trust concepts, continuous verification, least privilege, and preparation for post quantum cryptography.
For evaluation purposes, useful questions include:
What information is encrypted? Where is it processed? Who controls authentication and keys? Where are identities and recordings stored? Which services remain external? Which functions continue operating if external connectivity becomes unavailable?
Insight 4: Encryption and infrastructure control address different risks. Encryption protects information, while infrastructure control determines where services, identities, metadata, recordings, and administrative functions are located.
Air Gapped and Disconnected Communications

Some protected networks are designed to operate without direct access to the public internet.
Such an environment can still contain internal servers, directories, conferencing, messaging, telephony, gateways, file repositories, and other applications.
The main architectural issue is dependency management.
Disconnected operation may require local availability of:
- authentication;
- DNS;
- certificates;
- databases;
- storage;
- media processing;
- monitoring;
- administration;
- licensing mechanisms;
- update procedures.
A product described as self hosted can still depend on external systems for some functions. These dependencies should therefore be identified before deployment.
Interoperability and Existing Infrastructure
Defense related organizations can operate several generations of communication and information systems simultaneously.
Existing environments may include:
- radio networks;
- PBX systems;
- satellite terminals;
- dispatch platforms;
- hardware video endpoints;
- MCUs;
- directories;
- mobile devices;
- command applications;
- gateways.
Modernization can therefore require integration between existing and new infrastructure.
Common integration technologies can include:
- SIP;
- H.323;
- radio over IP;
- Ethernet;
- RTP;
- RTSP;
- APIs;
- LDAP;
- federation.
Protocol support should not be treated as proof of complete compatibility. Authentication, codecs, security modes, addressing, and optional protocol extensions can differ between implementations.
Testing should therefore be carried out within the actual environment for which a system is intended.
Examples of Defense Communication Technologies and Platforms
The following products illustrate different technology categories. They are included as informational examples rather than as a ranking or procurement recommendation.
L3Harris Falcon IV
Falcon IV is a family of tactical radio products developed by L3Harris.
Public manufacturer materials describe handheld and manpack configurations supporting combinations of tactical voice, data, networking, satellite connectivity, and interoperability functions.
Within a layered communications model, this type of platform belongs primarily to the tactical edge and tactical networking layers.
Motorola Solutions Defense Communications
Motorola Solutions provides radio, interoperability, broadband communication, video, and software technologies used across public safety and government communication environments.
Its portfolio includes P25 based communications and technologies intended to connect radio systems with broadband networks and applications.
Within a defense communications architecture, these technologies can serve radio, installation communication, and interoperability roles.
Rohde & Schwarz SOVERON
SOVERON is a family of software defined radio technologies from Rohde & Schwarz.
The portfolio includes solutions intended for vehicle, portable, airborne, and stationary communication environments. Public product information also describes support for modern and legacy waveform integration.
The technology belongs primarily to the tactical radio and secure communications layers.
TrueConf Server and TrueConf Enterprise

TrueConf operates at the application and collaboration layer rather than the tactical radio or transport layer.
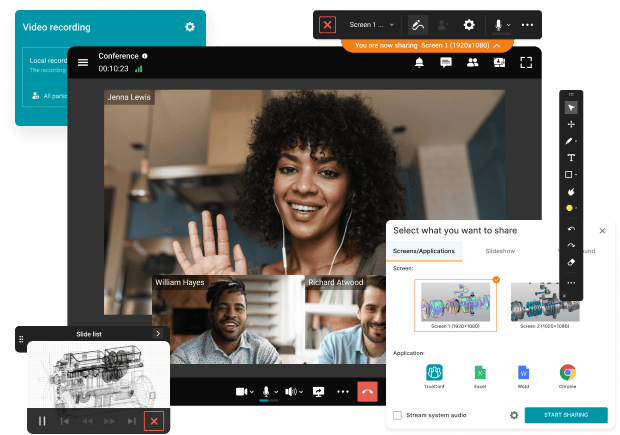
TrueConf Server can be deployed on organization controlled infrastructure and provides video conferencing, audio communication, personal and group chats, file exchange, screen sharing, conference recording, and centralized user management.
The platform can operate inside a private network without requiring continuous public internet connectivity.
TrueConf Server supports integration with LDAP compatible directories, including Active Directory, OpenLDAP, and FreeIPA. Its documentation specifies AES 256 media encryption and TLS 1.3 for native control traffic.
A built in gateway supports SIP, H.323, and RTSP, enabling integration with compatible PBX systems, video conferencing equipment, MCUs, and other communications infrastructure.
Paid deployments also support an offline registration procedure for installations where continuous external connectivity is unavailable.
Within the layered model described in this article, TrueConf can provide locally hosted video, messaging, and collaboration over an organization’s existing IP infrastructure.
TrueConf does not replace tactical radio, MANET, SATCOM, or a C2 system. Regulatory applicability and suitability for a particular protected information system depend on the deployment, information category, technical protection measures, certification requirements, and applicable legislation.
Boost your team’s productivity with TrueConf Server Free!
General Dynamics Mission Systems
General Dynamics Mission Systems develops communications technologies across areas including radios, tactical networking, satellite related communications, and network security.
Public materials describe systems for vehicle networking, radio communications, secure transport, and integration between different communication environments.
These technologies can occupy tactical edge, transport, gateway, and secure networking roles.
Thales SYNAPS
SYNAPS is a software defined tactical radio family from Thales.
Public materials describe configurations intended for land forces, including mounted communications and protected voice and data exchange.
Within the architecture discussed here, SYNAPS belongs primarily to the tactical radio and networking layers.
Persistent Systems MPU5
MPU5 is a networking and communication platform developed by Persistent Systems around its Wave Relay MANET technology.
Public specifications describe MANET networking together with IP connectivity, voice, video transport, and onboard computing functions.
This places MPU5 primarily within the tactical edge and mobile IP networking layers.
Cisco Webex for Defense
Cisco Webex for Defense represents a hosted collaboration model intended for supported U.S. Department of Defense environments.
Public Cisco documentation describes an Impact Level 5 authorized environment providing collaboration functions such as voice, video, meetings, messaging, and presence.
Its architectural role is different from tactical radio and MANET systems because it operates primarily at the hosted collaboration layer.
Defense Communication Technologies Compared by Role
|
Example |
Primary technology layer |
Typical role |
|---|---|---|
|
L3Harris Falcon IV |
Tactical radio and networking |
Mobile tactical communications |
|
Motorola Solutions |
Radio and interoperability |
Installation and multi network communications |
|
Rohde & Schwarz SOVERON |
Software defined radio |
Tactical voice and data |
|
TrueConf Server |
Collaboration |
Locally hosted video, messaging, and IP communications |
|
General Dynamics |
Tactical networking and secure transport |
Mobile and protected communications |
|
Thales SYNAPS |
Software defined radio |
Mounted and tactical communications |
|
Persistent Systems MPU5 |
MANET and tactical IP |
Mobile networking |
|
Cisco Webex for Defense |
Hosted collaboration |
Authorized cloud based collaboration |
The technologies in this table are not necessarily substitutes for one another. Several categories can form part of the same communications architecture.
Which Technology Category Addresses Which Requirement?
|
Requirement |
Relevant technology category |
|---|---|
|
Dismounted voice and tactical data |
Tactical radio |
|
Communication between moving network nodes |
MANET |
|
Beyond line of sight connectivity |
Satellite or long range radio transport |
|
Headquarters video and messaging |
Collaboration platform |
|
Isolated collaboration environment |
Locally hosted applications and identity infrastructure |
|
Existing SIP or H.323 equipment |
Compatible communication gateway |
|
Interconnection between heterogeneous networks |
Interoperability gateway |
|
Multiple independent communication paths |
Resilient multi path architecture |
|
Common operational picture |
C2 or C4ISR applications |
|
Hosted enterprise collaboration |
Approved hosted collaboration environment |
The purpose of this matrix is to separate technology categories according to their role rather than to rank specific products.
How to Evaluate a Defense Communication Architecture?

A useful evaluation process starts with operating conditions rather than individual products.
Define the environment
Identify where communication is required, for example:
- headquarters;
- fixed facilities;
- mobile command environments;
- vehicles;
- vessels;
- aircraft;
- mobile personnel;
- remote sites;
- isolated networks.
Different environments create different requirements for connectivity and applications.
Map the information types
Determine whether the system needs to transport:
- voice;
- video;
- text;
- files;
- location data;
- sensor information;
- telemetry;
- situational information;
- command data.
This affects bandwidth, endpoints, applications, storage, and security requirements.
Identify availability requirements
Determine which functions must remain available if individual communication services or infrastructure components become unavailable.
This can expose dependencies that are not visible in a normal feature comparison.
Identify external dependencies
For applications and infrastructure, review dependencies such as:
- authentication;
- licensing;
- certificates;
- DNS;
- updates;
- storage;
- media processing;
- monitoring;
- administration.
This is particularly relevant to disconnected systems.
Verify interoperability
Compatibility should be checked against the specific hardware, protocols, security configurations, directories, PBX systems, video endpoints, and gateways used in the target infrastructure.
Separate transport from applications
Radio, MANET, SATCOM, fiber, and other network technologies move information.
Messaging, video conferencing, telephony, and command applications use those networks.
Separating these roles makes system dependencies and integration boundaries easier to understand.
Common Evaluation Mistakes
One common mistake is evaluating an application without considering the network conditions in which it will operate.
Another is treating encryption as the complete security architecture. Authentication, administrative access, endpoint protection, software integrity, storage, and network segmentation can also affect system security.
A third mistake is confusing several communication interfaces with independent resilience. Multiple services can still depend on one underlying network or infrastructure component.
Another common issue is underestimating integration with existing systems. Legacy equipment, directories, telephony, video infrastructure, and security controls can significantly affect deployment requirements.
When an On-Premises Communication Platform Is Relevant?

An on-premises collaboration platform can be considered when an organization requires local control of application infrastructure.
Possible scenarios include:
- communication inside a private network;
- disconnected operation;
- local storage of application data;
- local directories;
- integration with existing telephony or video systems;
- internal administration;
- restricted external connectivity.
On-premises deployment alone does not establish compliance with security or regulatory requirements.
Suitability depends on the information being processed, system classification, applicable legislation, security controls, certification requirements, and the way the solution is configured and operated.
Conclusion
A defense communication system is a layered architecture connecting endpoints, transport networks, secure networking, collaboration applications, command systems, identity services, and management infrastructure. Tactical radio, MANET, SATCOM, secure IP, collaboration software, and C4ISR technologies address different functions within that architecture.
System evaluation should therefore start with information flows, operating conditions, security boundaries, integration requirements, external dependencies, and availability requirements. The central question is not which product offers the most functions, but whether the complete communication architecture provides the required capabilities within the technical, organizational, and regulatory conditions of the intended deployment.
Empower your video conferencing experience with TrueConf!
FAQ
What is a defense communication system?
A defense communication system is a combination of hardware, software, networks, and security controls used to exchange voice, video, messages, files, sensor information, and operational data. It can include tactical radios, MANET, SATCOM, secure IP networks, collaboration applications, and command systems.
What is the difference between a defense communication system and C4ISR?
Defense communications provide connectivity and information exchange used by C4ISR. C4ISR is broader because it also includes command, computing, intelligence, surveillance, reconnaissance, and systems that process or present operational information.
What is MANET in defense communications?
MANET stands for Mobile Ad Hoc Network. It allows network nodes to establish connectivity without relying on conventional fixed base station infrastructure, which can be useful in mobile environments.
Can a defense communication system work without internet access?
Some communication technologies and locally deployed applications can operate without public internet access. A fully disconnected environment also requires critical dependencies such as authentication, storage, administration, licensing, and name resolution to be available locally.
What is PACE in military communications?
PACE stands for Primary, Alternate, Contingency, and Emergency. It is a planning concept based on maintaining different communication methods for important processes rather than depending on only one path.
Is encryption enough to secure defense communications?
No. Encryption addresses only part of the security model. Identity management, authentication, access control, key management, endpoint protection, network segmentation, administration, software integrity, and data storage also need to be considered.
What should be evaluated first when selecting a communication architecture?
Start with the environment, users, information types, network conditions, security boundaries, existing infrastructure, availability requirements, and applicable regulatory requirements. Individual products can then be evaluated against those conditions.
About the Author
Diana Shtapova is a product specialist and technology writer with three years of experience in the unified communications industry. At TrueConf, she leverages her deep product expertise to create clear and practical content on video conferencing platforms, collaboration tools, and enterprise communication solutions. With a strong background in product research and user-focused content development, Diana helps professionals and businesses understand core product features, adopt new technologies, and unlock the full potential of modern collaboration software.
Follow us on social networks