
Data Leakage Prevention Best Practices: 15 Tips
Data leakage prevention best practices are the policies, technologies, and operational controls organizations use to stop sensitive information from reaching unauthorized users, applications, or destinations. The most effective strategies combine data discovery, classification, least-privilege access, Data Loss Prevention (DLP) software, endpoint security, cloud monitoring, employee awareness, and continuous policy testing. These measures protect confidential information whether it is stored in a database, exchanged through corporate messaging, uploaded to cloud storage, or submitted to an AI application.
For enterprises, preventing data leakage is not simply about blocking file transfers. Employees need to exchange information with customers, colleagues, and partners every day. Overly restrictive controls can disrupt legitimate operations, while policies that only generate alerts may detect incidents after confidential information has already left the organization. An effective prevention program must distinguish approved business activities from actions that create unnecessary exposure.
The best approach is to identify critical data, understand how it moves, and enforce protection at the moment a risky action occurs. Organizations should start with high-value information, apply consistent classification rules, secure access to sensitive systems, and introduce DLP controls across the communication channels employees actually use. Dedicated solutions such as Microsoft Purview, Forcepoint, Netskope, and Proofpoint address different parts of this process, while corporate communication platforms such as TrueConf Enterprise can extend DLP inspection to supported messaging workflows.
Data Leakage Prevention Best Practices at a Glance
|
Best practice |
What it prevents? |
Recommended approach |
|---|---|---|
|
Discover sensitive information |
Unprotected or forgotten confidential data |
Scan repositories, endpoints, and cloud environments |
|
Classify business data |
Inconsistent protection policies |
Apply sensitivity labels and content identification |
|
Enforce least-privilege access |
Unnecessary access to confidential records |
Use role-based permissions and regular access reviews |
|
Deploy DLP controls |
Unauthorized information transfers |
Monitor and block sensitive data movement |
|
Protect employee endpoints |
Data copying to USB drives or unmanaged applications |
Use endpoint DLP, encryption, and device management |
|
Secure cloud collaboration |
Public links and excessive file sharing |
Apply cloud DLP and permission controls |
|
Protect corporate messaging |
Confidential information shared in inappropriate chats |
Inspect supported messages and attachments |
|
Control generative AI usage |
Sensitive prompts and document uploads |
Use approved AI services and AI-aware DLP |
|
Encrypt sensitive information |
Exposure during storage or transmission |
Apply encryption in transit and at rest |
|
Monitor insider risks |
Unusual or unauthorized employee activity |
Combine activity context with proportionate investigation |
|
Train employees |
Accidental disclosure and unsafe sharing |
Provide practical, scenario-based guidance |
|
Measure enforcement |
DLP systems that detect but fail to prevent leaks |
Track blocked transfers, false positives, and coverage gaps |
These practices work best as a coordinated program. A company may have strong endpoint protection but still expose customer records through public cloud links. Another may classify documents carefully but allow unrestricted copying into personal AI accounts. Prevention requires controls across the entire data lifecycle, not isolated security products.
What Is Data Leakage Prevention?

Data leakage prevention is the practice of identifying sensitive information and reducing the risk that it will be disclosed, accessed, or transferred outside authorized boundaries. It includes technical tools such as DLP software, but also requires data governance, identity management, employee procedures, incident response, and regular security assessments.
The terms data leakage prevention and data loss prevention are often used interchangeably in enterprise cybersecurity. Both commonly use the abbreviation DLP, although data loss can also refer to deletion or unavailability, which is primarily addressed through backup and recovery.
What Causes Data Leakage?
Confidential information can leave an organization through several pathways.
Accidental disclosure occurs when employees make mistakes, such as sending a document to the wrong recipient, creating an unrestricted sharing link, or uploading sensitive information to an inappropriate application.
Insider misuse involves unauthorized actions by individuals who already have access to corporate systems. These incidents may involve deliberate data theft, excessive downloads, or transfers to personal accounts.
External compromise occurs when attackers gain access to accounts, devices, or infrastructure and extract information.
Misconfiguration can expose information without a conventional intrusion. A publicly accessible cloud repository, incorrectly configured file share, or excessive access permission may make confidential records available to unintended parties.
The prevention strategy differs for each scenario. Technical blocking can stop certain transfers, but access management, configuration reviews, and employee awareness are also essential.
Why Are Data Leakage Prevention Best Practices Important?

Sensitive information now moves through more systems than traditional office networks were designed to protect.
An employee may download a report from a database, edit it on a laptop, share it through a corporate messenger, and upload a summary to an AI application. Each step may be part of legitimate work, yet each also introduces an opportunity for unauthorized disclosure.
Data leakage can create financial, operational, legal, and reputational consequences. Organizations may lose intellectual property, expose customer records, violate contractual confidentiality obligations, or face regulatory investigations.
Strong prevention practices help reduce these risks while making information handling more predictable.
Business Benefits of Effective DLP
The most immediate benefit is reducing accidental exposure. A well-configured DLP policy can warn an employee about a sensitive attachment or block an unauthorized transfer before the information reaches its destination.
Data leakage prevention also improves visibility into business workflows. Security teams can identify where confidential information is stored, which applications employees use, and where access permissions are unnecessarily broad.
For organizations operating in regulated industries, DLP provides evidence that information handling controls exist and are being applied. However, deploying DLP does not automatically establish compliance with GDPR, HIPAA, PCI DSS, or other requirements.
Another important advantage is protecting intellectual property. Source code, engineering documentation, product designs, research materials, and confidential strategies may not contain obvious personal identifiers, but their unauthorized disclosure can cause substantial commercial harm.
15 Data Leakage Prevention Best Practices
The following practices provide a framework for protecting information across corporate infrastructure, employee devices, cloud services, and collaboration applications. Each recommendation should produce a measurable change in how sensitive information is managed, rather than simply add another security rule.
1. Discover and Inventory Sensitive Data
The first step in preventing data leakage is understanding where sensitive information exists.
Businesses frequently store confidential material across databases, employee laptops, shared folders, cloud repositories, email archives, and collaboration tools. Over time, files are copied, exported, and retained in locations that were never intended for long-term storage.
Data discovery tools can identify information matching predefined categories, document fingerprints, or other classification criteria. The results help security teams establish which repositories contain high-value information and which require additional protection.
For example, a healthcare organization may discover patient records in spreadsheets stored outside its approved clinical systems. A manufacturing company may find technical drawings in a shared folder accessible to employees who no longer work on the relevant project.
A useful inventory should identify the information owner, storage location, sensitivity, authorized users, and applicable retention requirements. Organizations should also record whether the information is actively used or can be archived or deleted according to approved retention rules.
In February 2026, NIST published the initial public draft of SP 1800-39, Data Classification Practices, emphasizing the importance of discovering, identifying, and labeling unstructured data. The guidance illustrates why organizations need to understand their information before introducing more advanced security controls.
Practical outcome: A maintained inventory of critical data repositories, assigned business owners, documented sensitivity, and a list of locations requiring remediation.
2. Establish Consistent Data Classification
Once sensitive information has been discovered, it should be classified according to business value and disclosure risk.
A practical classification model often includes four levels.
|
Classification |
Description |
Example |
Typical protection |
|---|---|---|---|
|
Public |
Approved for unrestricted distribution |
Published marketing materials |
Standard access and integrity controls |
|
Internal |
Intended for employees and approved partners |
Internal operating procedures |
Corporate access controls |
|
Confidential |
Disclosure could harm the organization |
Customer reports and financial projections |
Restricted sharing and DLP inspection |
|
Restricted |
Highly sensitive or regulated information |
Credentials, trade secrets, regulated records |
Strict access, monitoring, and transfer restrictions |
Classification should influence how employees handle information. A public document may be shared through ordinary business channels, while a restricted engineering design may require approved storage, named recipients, and additional authorization for external transfer.
Modern DLP systems can detect sensitive information using exact data matching, regular expressions, document fingerprinting, and machine learning. However, automated classification is not always sufficient. Business owners should help identify confidential material that lacks recognizable technical patterns, such as strategic plans or unpublished research.
Classification becomes operationally useful when it is connected to clear handling rules. For example, an organization can define that Restricted documents must remain in approved repositories, cannot be uploaded to personal accounts, and require authorization before external sharing.
The classification model should also address documents containing multiple data categories. A file containing both public product information and confidential customer records may require protection according to its most sensitive contents.
Practical outcome: An approved classification policy, identifiable data labels, documented handling requirements, and DLP rules linked to those classifications.
3. Apply Least-Privilege Access Controls
One of the most effective ways to prevent data leakage is to reduce unnecessary access to confidential information.
The principle of least privilege means employees receive only the permissions needed to perform their responsibilities.
A payroll specialist may need access to employee compensation records, but that access does not justify permission to download unrelated customer databases. Similarly, a contractor may require access to a specific project folder without needing visibility into the organization’s entire document repository.
Role-based access controls, identity management, and periodic permission reviews help enforce these boundaries. Organizations should pay particular attention to shared administrator accounts, inactive employee identities, external guests, and service accounts with broad privileges.
Multi-factor authentication reduces the likelihood of unauthorized account access, while timely account deactivation limits exposure after employees or contractors leave.
Access reviews should also produce a clear result. A department manager can receive a list of users with access to a confidential repository and confirm which permissions remain necessary. Unjustified access can then be removed, with the decision recorded for future review.
Practical outcome: Defined access roles, named data owners, completed permission reviews, and fewer unnecessary accounts with access to sensitive information.
4. Implement Data Loss Prevention Policies Across Key Channels
DLP software is a central technical component of a data leakage prevention program.
It identifies protected information and evaluates whether a particular action violates organizational policy. Common enforcement points include email, endpoint devices, cloud storage, web applications, and corporate collaboration systems.
For example, an organization may allow employees to access customer records within an approved CRM but prevent those records from being exported to personal storage.
A well-designed policy should consider the content, user, destination, and context of the action rather than relying exclusively on keywords.
The response can also vary by risk. A low-risk action may generate a warning, while an attempt to transfer highly restricted information to an unauthorized destination may be blocked automatically.
DLP deployment should begin with the most important information pathways rather than attempting to cover every possible activity simultaneously.
An effective first policy might identify an actual protected customer dataset and prevent its transfer to external personal email accounts. After validating this rule, the organization can expand protection to additional destinations or types of confidential information.
Practical outcome: Tested policies for prioritized data transfers, documented enforcement actions, and evidence that selected prohibited activities are blocked before completion.
5. Secure Endpoints and Removable Storage
Employee laptops and workstations are common points where confidential information is accessed, copied, and transferred.
Endpoint DLP helps monitor supported actions such as file copying, printing, uploading, and transferring data to removable devices.
Organizations should combine these controls with device encryption, operating system updates, endpoint detection and response, and centralized device management.
Removable storage policies should reflect actual business requirements. A company may prohibit unapproved USB drives while allowing encrypted corporate storage devices. Another may permit selected employees to transfer specific file categories under controlled conditions.
Remote work makes endpoint protection particularly important because sensitive information may be handled outside the corporate network.
Security policies should continue to operate on managed devices when employees are working from home or traveling, subject to the capabilities of the endpoint solution.
Testing should include approved and unapproved devices, offline activity where supported, and transfers through the applications employees actually use.
Practical outcome: Managed endpoints with device encryption, defined removable media restrictions, and verified protection for sensitive files outside the office network.
6. Protect Cloud Storage and SaaS Collaboration
Cloud applications make information easy to access and share, but they can also create unintended exposure.
A confidential document may become available outside the organization through an unrestricted sharing link, excessive guest permissions, or synchronization with an unmanaged account.
Cloud DLP and related security controls can identify sensitive files, evaluate sharing settings, and restrict certain activities.
Organizations should distinguish between two methods of protection.
Inline inspection evaluates supported transfers as they occur. It can stop a prohibited upload before completion when the traffic passes through an appropriate inspection point.
API-based scanning examines information through integrations with cloud applications. It is particularly useful for discovering existing exposure, such as confidential documents shared publicly several weeks earlier.
Both approaches are useful, but they do not provide identical protection.
A cloud security program should also include regular permission reviews, removal of unused external accounts, and controls for personal cloud storage services.
For example, administrators can periodically generate a report of externally accessible documents marked Confidential or Restricted. Business owners can confirm which sharing permissions are legitimate and remove unnecessary access.
Practical outcome: Controlled external sharing, documented exceptions, and a regularly reviewed inventory of sensitive files accessible to external users.
7. Secure Corporate Messaging and File Exchange
Corporate messaging has become an important channel for exchanging business information.
Employees share customer details, financial reports, contracts, and technical documentation through direct chats and group conversations. Yet some organizations still apply stronger DLP controls to email than to internal messaging.
This creates a protection gap. A confidential document can be sent to an inappropriate chat even when the messaging application itself is authorized.
Organizations should evaluate whether their communication platforms support message inspection, file scanning, identity management, and integration with external security systems.
For example, Microsoft Purview can apply DLP policies to supported Microsoft Teams chat and channel messages. TrueConf Enterprise supports integration with external DLP systems through ICAP, allowing supported messages and attachments to be inspected according to corporate policies.
However, security teams must distinguish between detecting a violation and preventing delivery. A system may log a prohibited message without blocking it if that is the configured response.
An effective test should cover both ordinary text and file att
achments. For example, administrators can verify whether confidential customer information pasted into a supported chat is detected and whether a restricted document reaches an unauthorized recipient.
Practical outcome: Documented communication policies and verified inspection and enforcement behavior for supported messaging workflows.
8. Establish Clear Rules for Generative AI
Generative AI introduces a new category of data leakage risk.
Employees may submit source code, customer information, legal documents, financial reports, or internal instructions to external AI applications. Sometimes these transfers are intentional. In other cases, employees may not realize that an AI prompt contains confidential information.
An effective policy should identify approved AI applications, permitted data categories, and prohibited activities.
For example, an employee might be allowed to use an approved AI assistant to summarize public research but prohibited from submitting customer databases through a personal account.
AI-aware DLP tools can inspect supported prompts, uploads, and application activity. However, coverage differs between services. Some tools can block selected uploads in real time, while others primarily provide monitoring or investigation after an event.
Organizations should test the specific AI workflows employees use rather than assume that general web DLP automatically protects every AI interaction.
A practical AI usage policy can distinguish public information, ordinary internal information, and restricted business content. It should also explain how employees can request authorization when a legitimate workflow requires sensitive data to be processed by an AI system.
Practical outcome: An approved AI application inventory, explicit data handling rules, and tested controls for relevant prompts and file uploads.
9. Encrypt Sensitive Data in Transit and at Rest
Encryption helps protect information when it is stored or transmitted.
Transport encryption reduces exposure during communication between systems. Encryption at rest protects stored information against unauthorized access when the appropriate keys remain secure.
Full-disk encryption is particularly important for employee laptops and portable devices.
However, encryption alone does not prevent every form of leakage.
An employee may send an encrypted document to an unauthorized recipient who can decrypt it. A compromised endpoint may also expose information after an application has opened it.
For this reason, encryption should be combined with DLP, access controls, and endpoint protection.
Organizations must also maintain appropriate key management and recovery procedures.
Practical outcome: Approved encryption requirements for sensitive information, verified device and storage protection, and controlled access to encryption keys.
10. Monitor Insider Risk Without Treating Every Anomaly as Malicious
Insider-related data exposure can result from mistakes, compromised accounts, or deliberate misuse.
DLP systems may identify unusual information transfers, while insider risk tools provide additional context about user activity.
For example, an employee who suddenly downloads a large volume of confidential documents and uploads them to an unfamiliar external service may require investigation. However, the activity may also be related to an approved project or operational task.
Security teams should evaluate the content, destination, recent activity, and business justification before drawing conclusions.
Monitoring should be proportionate and consistent with applicable privacy and employment requirements.
The objective is to identify meaningful risks while avoiding unnecessary surveillance or disruptive false positives.
Practical outcome: Defined investigation thresholds, documented escalation procedures, and proportionate review of suspicious data movement.
11. Reduce Shadow IT and Unmanaged Application Usage
Employees sometimes use unauthorized applications because they offer a faster or more convenient way to complete work.
Examples include personal file-sharing services, consumer messengers, unmanaged collaboration platforms, and external AI tools.
Blocking these services without providing suitable alternatives can encourage workarounds.
Organizations should identify commonly used applications, evaluate their security implications, and provide approved tools that meet legitimate employee needs.
Cloud access monitoring, endpoint controls, and application inventories can help identify unsupported data transfer pathways.
A practical governance process distinguishes approved applications, applications requiring additional assessment, and prohibited services. It should also give employees a clear way to request new tools when existing solutions do not meet their requirements.
For example, if employees regularly upload large technical files to personal cloud accounts, the underlying problem may be that the approved corporate file-sharing system does not support their workflow.
Providing a suitable managed alternative can reduce exposure more effectively than repeatedly issuing warnings.
Practical outcome: A maintained application inventory, documented approval rules, identified high-risk services, and approved alternatives for common employee workflows.
12. Use Context-Aware Enforcement Instead of Universal Blocking
A sensitive document is not necessarily being mishandled every time an employee opens or transfers it.
A financial report may be legitimately shared with an approved auditor but should not be uploaded to a personal cloud account.
Context-aware DLP evaluates information sensitivity alongside the user, destination, application, and business activity.
This allows organizations to apply different actions to different scenarios.
For example, a policy may permit internal sharing, require justification for approved external collaboration, and block transfers to unknown destinations.
Such flexibility reduces unnecessary interruptions while maintaining protection for critical information.
Practical outcome: Policies that distinguish routine approved activity from high-risk transfers and apply proportionate enforcement.
13. Train Employees With Realistic Scenarios
Employee awareness remains important because not every risky action can be recognized automatically.
Training should explain which information is confidential, where it may be stored, how to verify recipients, and which applications are approved for external sharing.
Scenario-based guidance is generally more useful than abstract warnings.
For example, employees should understand what to do when a customer requests an export of personal information, when a colleague asks for credentials through chat, or when an AI application requests an internal document.
DLP notifications can reinforce these practices at the moment an employee attempts a risky action.
Clear explanations improve the likelihood that employees understand and follow policies rather than treating security controls as arbitrary obstacles.
Practical outcome: Role-specific training, documented handling guidance, and regular exercises covering common disclosure scenarios.
14. Test DLP Policies Before Enabling Strict Enforcement
Poorly configured DLP can interrupt legitimate work while leaving important channels unprotected.
Organizations should validate policies against realistic business workflows.
For example, a test may involve sending a customer spreadsheet to an unauthorized recipient, uploading a classified file to personal storage, copying restricted information to removable media, or sharing confidential content through a corporate chat.
The test should establish whether the activity was detected, whether it was blocked before completion, and whether the user received useful guidance.
Where the risk allows, new policies can begin in monitoring mode. After reviewing false positives and approved use cases, administrators can introduce stronger enforcement.
High-confidence violations involving particularly sensitive information may justify immediate blocking.
Tests should also cover failure conditions. If a DLP service becomes unavailable, the organization should know whether supported transfers are blocked, delayed, or allowed.
Practical outcome: Completed test scenarios, documented policy behavior, identified exceptions, and validated enforcement before broader rollout.
15. Continuously Measure and Improve DLP Effectiveness
Data leakage prevention is not complete when the software is installed.
Applications change, new cloud services are adopted, employees develop new workflows, and security risks evolve.
Organizations should review protection coverage, policy exceptions, incident trends, and actual prevention outcomes.
The most useful metrics are not necessarily those producing the largest numbers.
A security dashboard showing thousands of DLP alerts may look impressive, but it does not prove that sensitive information was prevented from leaving the organization.
Better indicators include the proportion of prohibited transfers blocked before completion, false positive rates, critical data coverage, and the time required to investigate meaningful incidents.
For example, a company could define a quarterly objective to verify that every prioritized data transfer scenario has an active control and a recorded test result. It can then measure whether coverage improves without an unacceptable increase in false positives.
Practical outcome: A recurring DLP effectiveness report showing protection coverage, successful blocking tests, significant incidents, unresolved gaps, and assigned remediation owners.
Insight 1.
Data Leakage Prevention begins with business context, not blocking rules.
A common mistake is deploying DLP software before understanding how employees use sensitive information.
An organization may establish a policy prohibiting all external transfers of confidential documents. However, its legal, finance, and customer support departments may legitimately need to share selected records with approved external parties.
The policy then creates a conflict between security and ordinary business operations.
Employees request exceptions, administrators disable restrictions, and the organization gradually loses confidence in its DLP program.
The strongest data leakage prevention policies distinguish authorized information sharing from unacceptable disclosure.
This requires business owners to participate in classification and policy design, not simply delegate every decision to the security department.
Data Leakage Prevention Statistics: What 2026 Research Shows?
Recent research suggests that deploying DLP software does not necessarily mean organizations are preventing sensitive data transfers effectively.
In October 2026, the Cloud Security Alliance published DLP in the AI Era, a survey of 433 IT and security professionals conducted in collaboration with Jazz.
The research found that 73% of respondents reported at least one confirmed data loss incident during the previous 24 months.
Among respondents who experienced data loss, only 16% reported that DLP blocked their most significant incident before information left the organization.
The study also identified important gaps in generative AI protection. Although 48% of respondents selected GenAI as a leading exfiltration risk, only 29% could routinely produce a 30-day report showing sensitive information sent to GenAI tools.
Cloud storage also remained a concern. While 41% identified cloud storage uploads as a leading exfiltration risk, only 19% reported strict blocking for that channel.
|
Finding |
2026 result |
Practical implication |
|---|---|---|
|
Respondents reporting a confirmed data loss incident in the previous 24 months |
73% |
Data exposure remains common among surveyed organizations |
|
Respondents with data loss whose DLP blocked their most significant incident before data left |
16% |
Detection does not necessarily translate into prevention |
|
Respondents identifying GenAI as a leading exfiltration risk |
48% |
AI workflows require dedicated assessment |
|
Respondents able to routinely report sensitive data submitted to GenAI over 30 days |
29% |
AI data movement visibility remains incomplete |
|
Respondents identifying cloud storage uploads as a leading risk |
41% |
Cloud sharing requires stronger policy coverage |
|
Respondents applying strict blocking to cloud storage uploads |
19% |
Enforcement is often weaker than perceived risk |
These are survey findings, not universal failure rates for DLP technology. They describe reported experiences and practices among the surveyed professionals.
The broader financial impact of information compromise is also significant. IBM’s Cost of a Data Breach Report 2026 reported an average global data breach cost of $4.99 million, an increase of 12% from the previous year.
Together, the studies reinforce an important distinction: data security programs should demonstrate that they can prevent important transfers, not merely show that monitoring tools are installed.
Insight 2.
The gap between detecting and preventing a leak is a security risk of its own.
Consider two organizations using DLP.
The first identifies an unauthorized file upload and creates an incident report after the transfer is completed. The second evaluates the same activity before completion and blocks the upload according to a verified policy.
Both systems may report that they detected a DLP violation, but only the second prevented the original disclosure.
Post-event detection still matters for investigation and remediation. It can help identify affected records, remove public access, and improve future controls.
However, a DLP program should report detection and prevention as separate outcomes.
This provides a clearer measure of whether the technology is reducing exposure or merely documenting it.
Data Leakage Prevention Best Practices by Environment

Different business environments require different combinations of controls. A strategy that works for corporate email may be insufficient for cloud collaboration, endpoint activity, or generative AI.
|
Environment |
Main exposure scenario |
Priority controls |
What to test |
|---|---|---|---|
|
Corporate email |
Confidential attachments sent externally |
Content classification, recipient restrictions, DLP blocking |
External delivery of restricted files |
|
Employee endpoints |
Files copied to unapproved devices |
Endpoint DLP, encryption, device policies |
USB, printing, and application transfers |
|
Cloud storage |
Sensitive documents shared publicly |
Cloud DLP, access reviews, sharing restrictions |
Public links and external guest access |
|
Corporate messaging |
Information sent to inappropriate chats |
Message inspection, file checks, permissions |
Text and attachment enforcement |
|
Generative AI |
Sensitive prompts and uploads |
Approved AI environments, AI-aware DLP |
Prompts, file uploads, and clipboard activity |
|
Databases |
Large unauthorized exports |
Least privilege, monitoring, export controls |
Bulk extraction and privileged access |
|
Remote work |
Information handled outside office networks |
Endpoint controls, identity protection, secure access |
Policy enforcement away from corporate networks |
This matrix provides a practical starting point for organizations introducing DLP. Security teams can prioritize environments according to the sensitivity of information, actual transfer volumes, and the potential consequences of disclosure.
Best Data Leakage Prevention Solutions in 2026
The most effective DLP technology depends on which information channels an organization needs to protect.
Some products offer broad enterprise protection across endpoints, network traffic, email, and cloud applications. Others specialize in particular environments or extend DLP through integration with a dedicated security engine.
The following ten solutions represent different approaches to implementing data leakage prevention best practices.
1. Microsoft Purview Data Loss Prevention
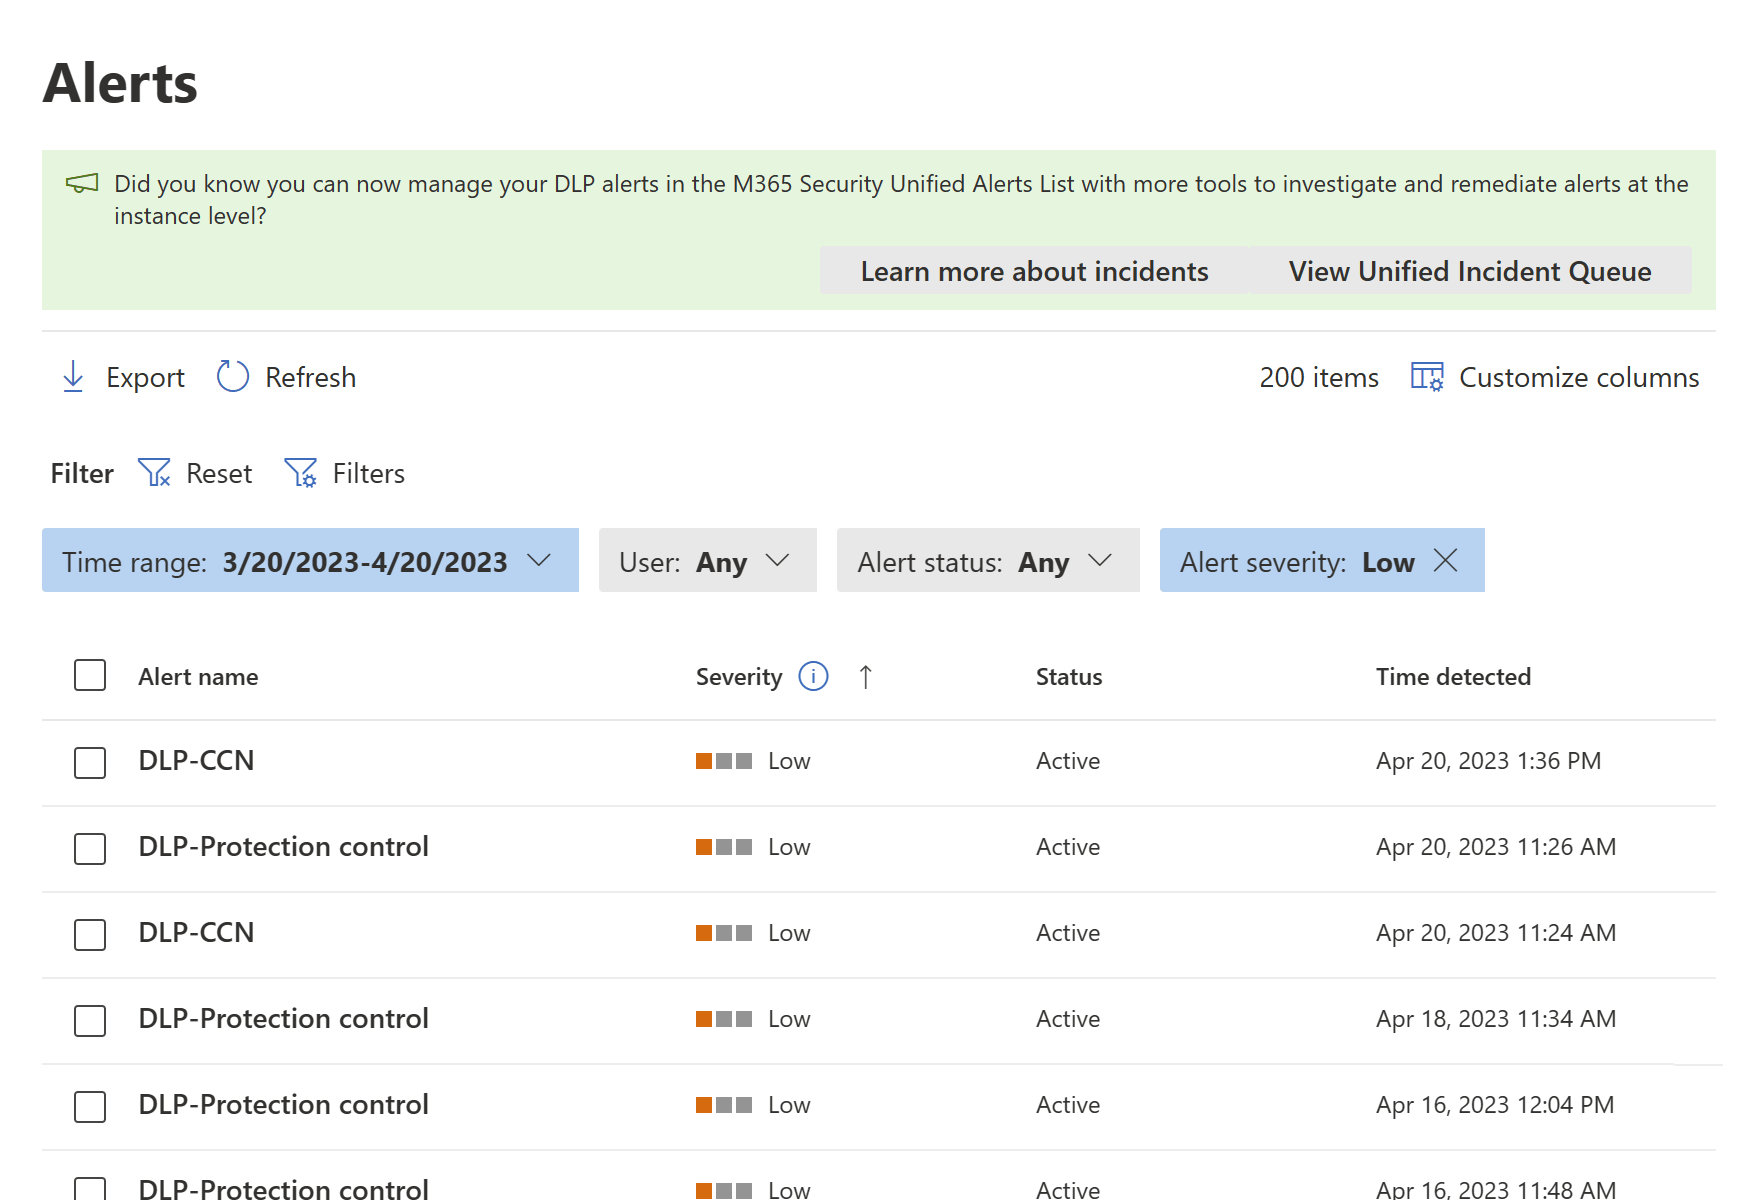
Best for: Organizations using Microsoft 365 that need centralized information protection across email, documents, Teams, endpoints, and supported AI workflows.
Microsoft Purview DLP integrates information classification and policy enforcement with Microsoft’s productivity and security environment.
Sensitive Information Classification
Purview includes predefined sensitive information types, custom detection rules, trainable classifiers, and sensitivity labels.
Organizations can identify structured personal information, payment data, and documents classified according to internal business policies.
For example, a financial institution may apply restrictions to documents containing protected customer information even when employees attempt to share them through different Microsoft 365 applications.
Microsoft 365 Protection
Purview supports DLP policies across Exchange Online, SharePoint, OneDrive, and supported Microsoft Teams chats and channel messages.
Administrators can identify confidential information and apply appropriate restrictions according to the activity and destination.
In Teams, message protection and file protection are handled through different supported locations and mechanisms. Organizations must verify that policies cover the exact communication workflows they want to secure.
Endpoint DLP
Microsoft Purview Endpoint DLP provides monitoring and enforcement on supported Windows and macOS devices.
Policies can address selected activities involving removable storage, printing, file transfers, and supported application interactions.
This helps protect documents even after employees download them from Microsoft 365 to managed computers.
Policy Tips and Overrides
Purview supports notifications that explain why an action is restricted.
Depending on the configured policy and activity, employees may be warned, blocked, or allowed to override a restriction with justification.
These options are useful for organizations introducing DLP gradually while maintaining legitimate external collaboration.
AI and Browser Protection
Microsoft Purview includes capabilities for supported Copilot experiences, cloud applications, and inline web traffic scenarios.
For example, organizations can evaluate whether sensitive information is being sent to unsupported AI services through managed browser or network workflows.
The available coverage depends on the product edition, prerequisites, and inspection method.
Business benefit: Microsoft Purview allows organizations to extend existing Microsoft 365 information protection policies across multiple employee workflows.
Strengths: Native Microsoft 365 integration, classification, endpoint DLP, Teams policies, user notifications, and supported AI protection.
Limitations: Licensing and technical prerequisites vary by workload. Non-Microsoft applications may require additional integrations or inspection components.
2. Forcepoint DLP
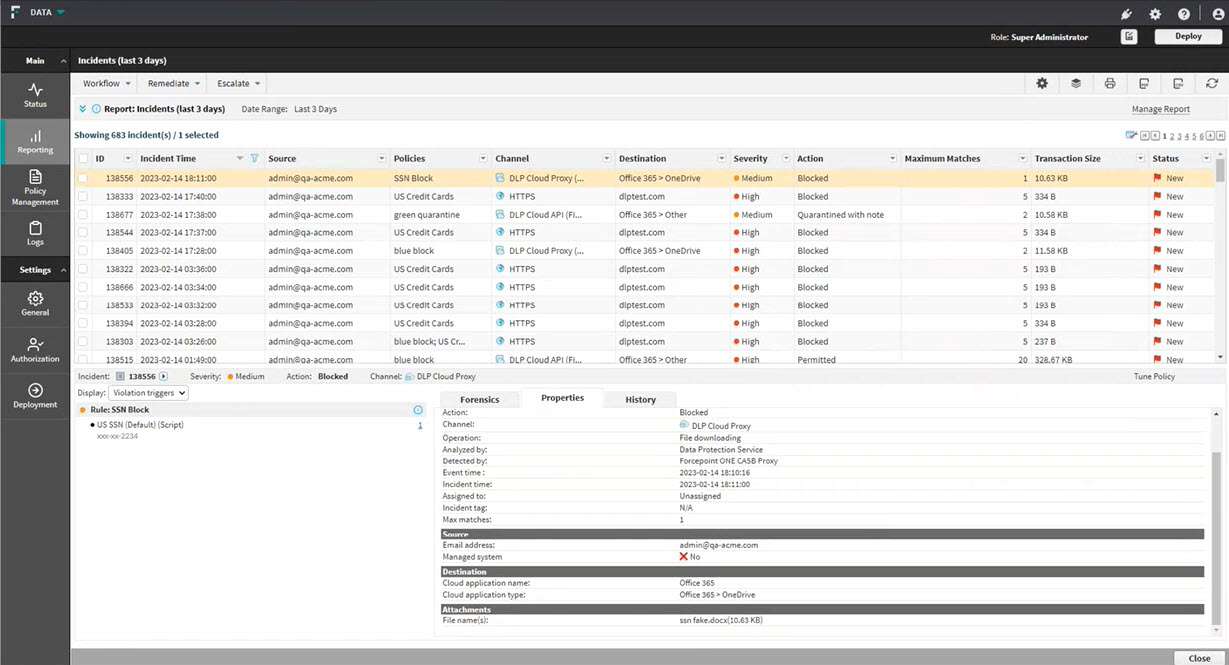
Best for: Large enterprises needing comprehensive protection across endpoints, email, network traffic, and cloud services.
Forcepoint DLP combines content detection, centralized policies, and behavioral context.
Advanced Content Identification
Forcepoint supports exact data matching, document fingerprinting, contextual analysis, and OCR.
These capabilities help identify sensitive information that ordinary keyword rules may not recognize.
A manufacturer can use document fingerprinting to protect confidential engineering documents, while a financial institution may use exact matching for protected customer records.
Unified Policy Management
Forcepoint allows organizations to coordinate protection rules across supported communication channels.
This helps businesses maintain consistent treatment of confidential information when employees move between email, endpoints, and cloud applications.
Risk-Adaptive Protection
Forcepoint’s risk-adaptive capabilities combine DLP with behavioral analytics to adjust responses according to supported user risk indicators.
Consider a finance employee who regularly exports an approved set of reports to an internal accounting system. That activity may present little reason for intervention.
If the same employee suddenly attempts to move a large volume of restricted records to an unfamiliar personal account, the combination of sensitive content, unusual destination, and behavioral context may justify a stronger response.
Depending on the configured capabilities, an organization can apply additional monitoring or enforcement to higher-risk behavior while preserving routine approved work.
The value of this approach depends on accurate behavioral context. Risk signals should be validated, and the organization should provide appropriate review mechanisms for legitimate unusual activities.
Endpoint and Network Enforcement
Forcepoint supports policies for selected endpoint activities, including removable storage, printing, and file transfers, alongside broader network and cloud protection.
These capabilities help organizations monitor information movement across hybrid infrastructure.
Business benefit: Forcepoint supports contextual DLP enforcement across complex enterprise environments.
Strengths: Advanced content identification, risk-adaptive protection, centralized policies, and broad channel coverage.
Limitations: Deployment complexity and behavioral policy tuning require experienced administration.
3. Netskope One DLP
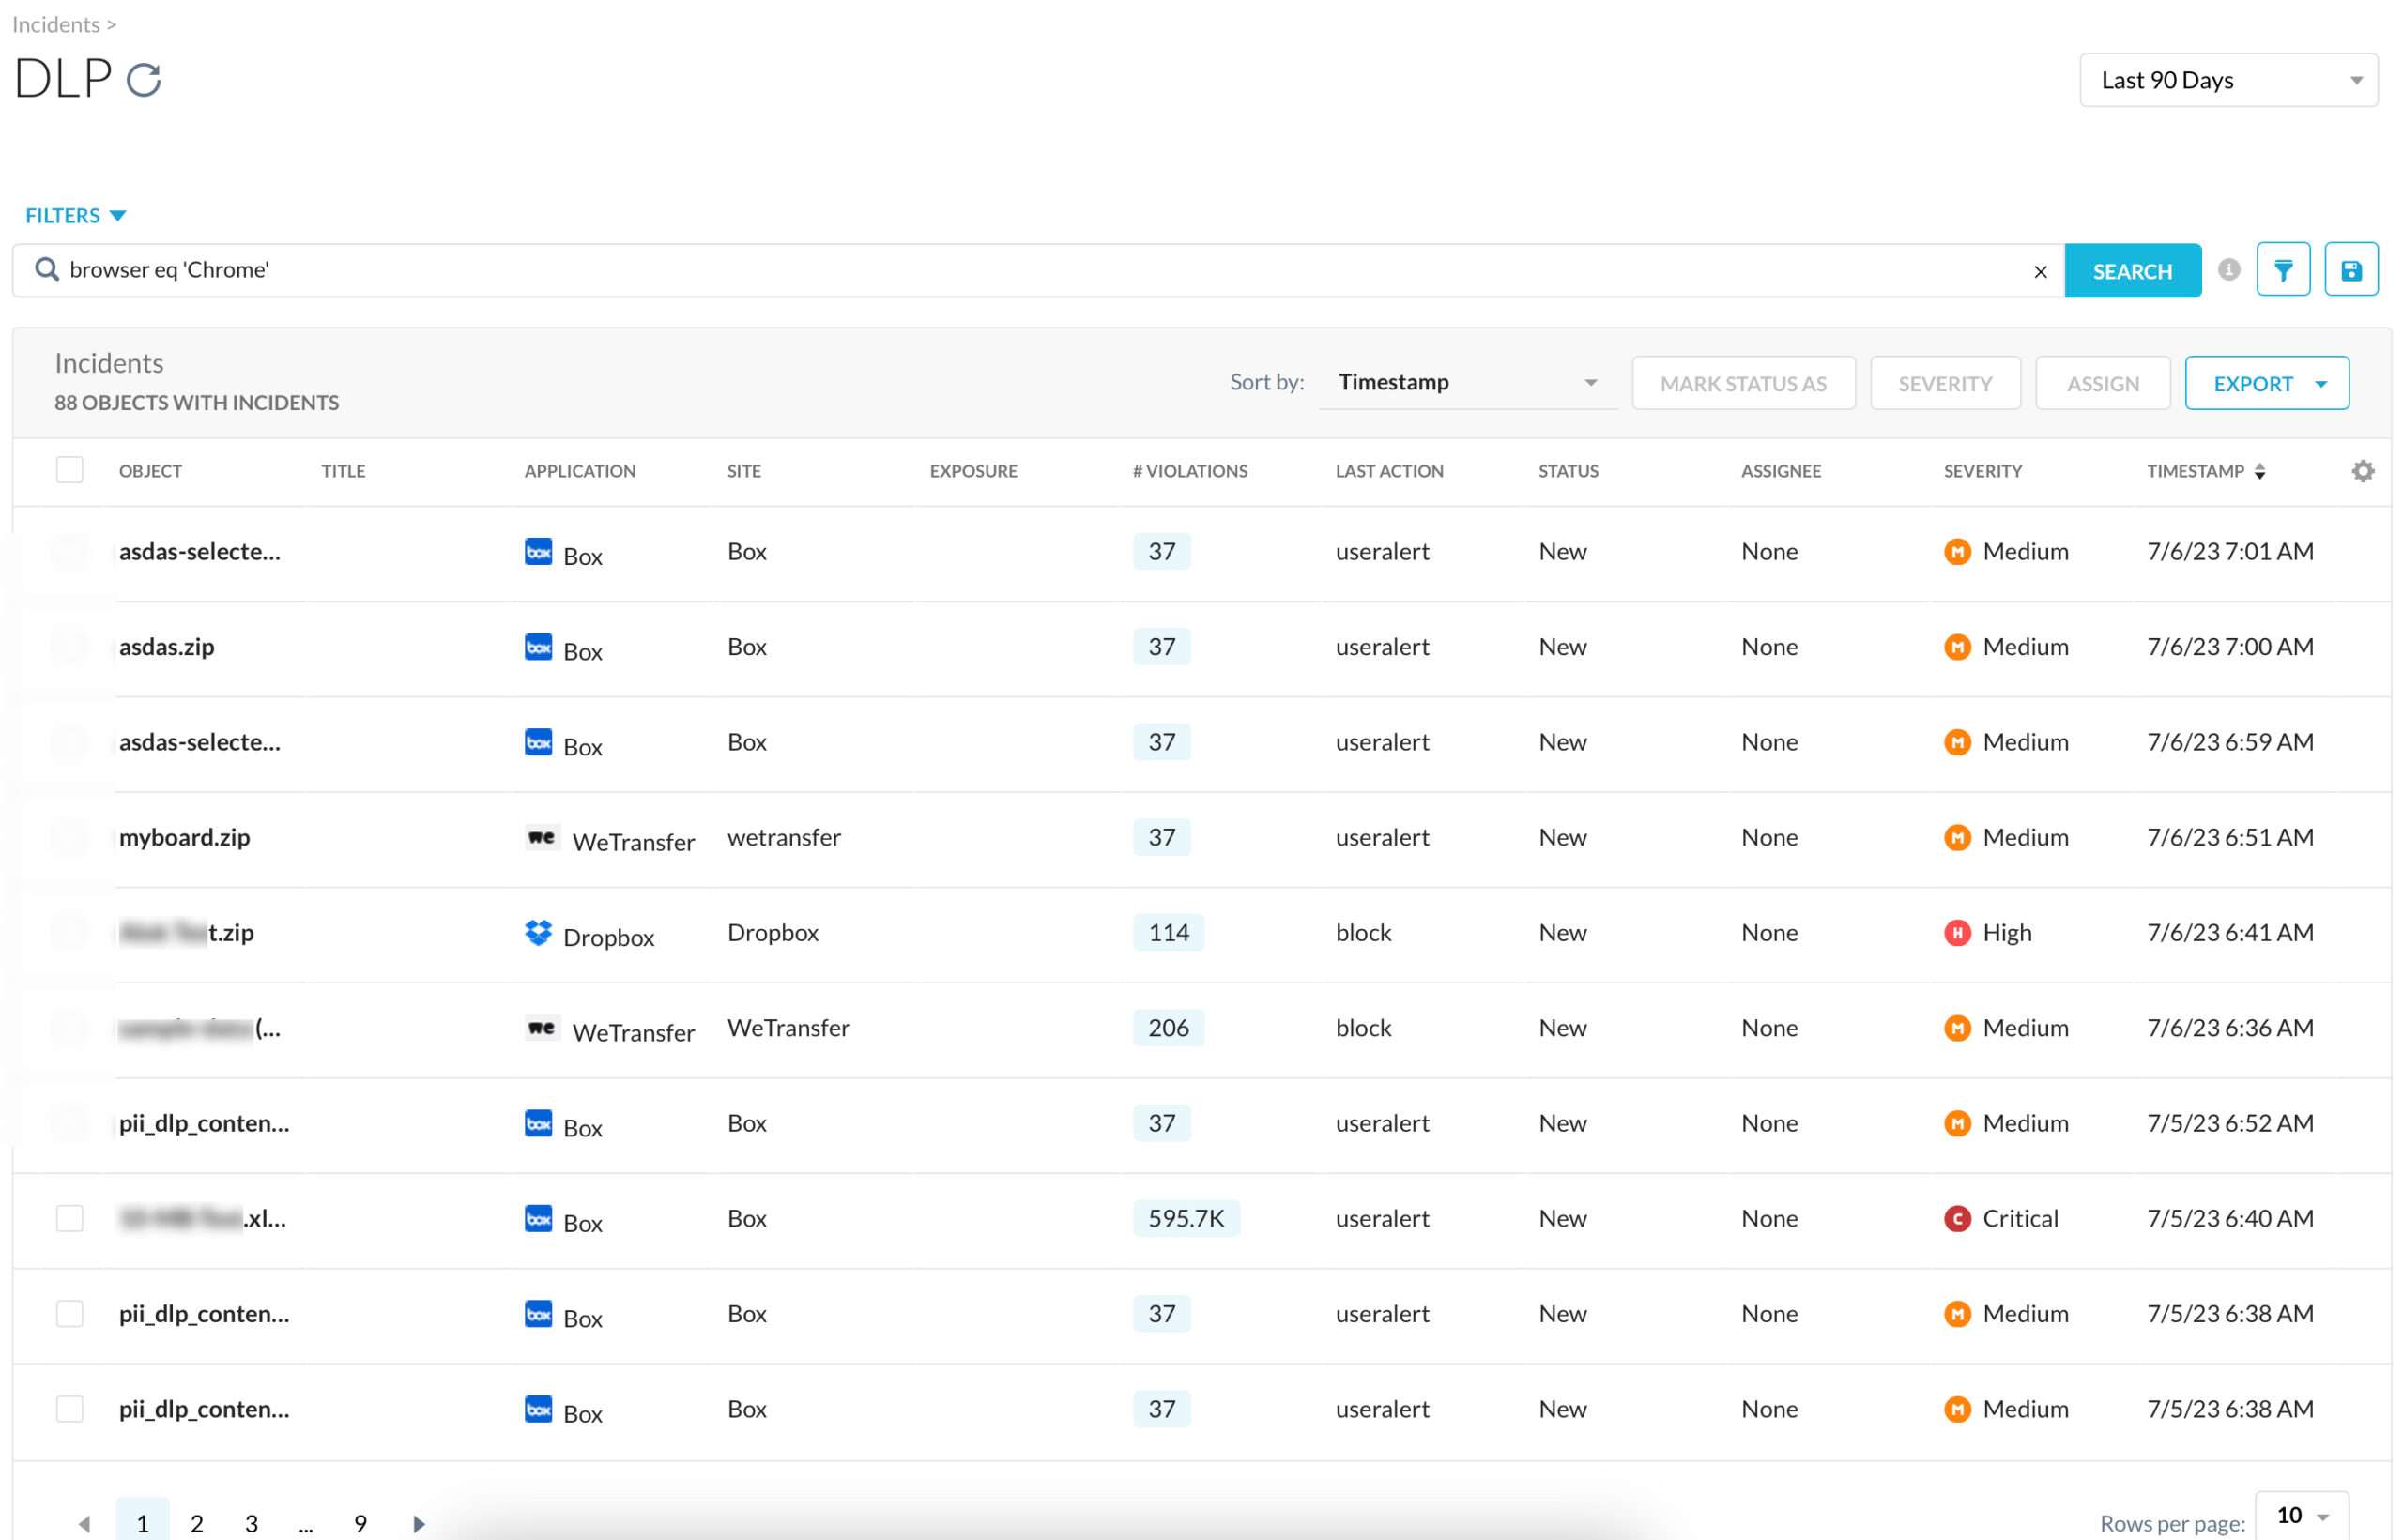
Best for: Cloud-first organizations that need consistent DLP across SaaS services, web applications, and supported endpoints.
Netskope One DLP is integrated with a broader cloud security architecture.
Content Classification
Netskope provides sensitive data identifiers, custom dictionaries, regular expressions, and classification capabilities.
Advanced licensing also supports techniques such as exact data matching, file fingerprinting, OCR, and machine learning-based classification.
These features help identify both structured customer records and unstructured documents.
Inline Cloud Protection
Netskope can inspect supported uploads and application activity as traffic passes through a configured inspection path.
This enables organizations to apply blocking policies before certain prohibited transfers are completed.
For example, a company may restrict uploads of confidential spreadsheets to unauthorized personal storage accounts.
API-Based Cloud Scanning
API integrations can evaluate sensitive information already stored in supported cloud repositories.
This helps identify publicly shared files, inappropriate permissions, and historical exposure.
Unlike inline inspection, API-based discovery may identify content after it has already reached the application.
Incident Investigation
Netskope includes incident management capabilities that help security teams review policy matches, user context, and data exposure.
A business can use this information to identify repeated sharing problems or refine overly broad policies.
Business benefit: Netskope combines cloud application visibility with preventive controls for supported data movement.
Strengths: SaaS coverage, inline inspection, API scanning, advanced classification, and incident workflows.
Limitations: Protection depends on inspection paths, application integrations, and selected licensing.
4. Proofpoint Enterprise DLP
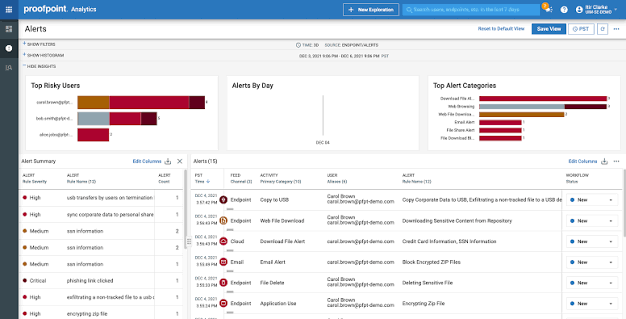
Best for: Organizations seeking to combine data protection with user behavior analysis and insider risk management.
Proofpoint Enterprise DLP focuses on identifying sensitive information and understanding the activities surrounding potential disclosure.
Email and Cloud Protection
Proofpoint provides controls for sensitive information exchanged through supported email and cloud applications.
Organizations can use these capabilities to reduce accidental external sharing and identify inappropriate document permissions.
Insider Risk Context
Proofpoint combines information about data movement with user activity signals.
For example, a sudden download of confidential records followed by an external upload may warrant investigation, especially when the behavior differs significantly from the user’s normal work.
Context can help security teams prioritize incidents, although unusual activity should not automatically be treated as proof of malicious intent.
Investigation and Response
A financial services company may detect that an employee downloaded a large number of confidential customer documents and subsequently transferred files to an unfamiliar external destination.
An ordinary content-based DLP alert might identify the confidential files but provide limited explanation of the surrounding activity.
By combining supported DLP events with user activity context, an investigation can examine the sequence of actions, identify affected documents, and assess whether the behavior differs from the employee’s authorized responsibilities.
Security analysts may discover an approved customer migration, an accidental use of the wrong account, or a genuinely unauthorized transfer attempt. Each outcome requires a different response.
Proofpoint’s investigation capabilities help analysts organize the available evidence and prioritize meaningful incidents. However, conclusions should depend on verified facts rather than a behavioral risk score alone.
AI-Related Data Protection
Proofpoint provides capabilities for identifying sensitive information in supported AI application workflows.
These controls can help address confidential documents or internal information submitted through prompts and uploads.
Business benefit: Proofpoint links DLP events with user context to improve investigation and incident prioritization.
Strengths: Email protection, insider risk visibility, cloud coverage, investigation tools, and AI-related controls.
Limitations: Effective deployment depends on integration coverage, suitable policy tuning, and responsible use of behavioral monitoring.
5. Zscaler Data Loss Prevention
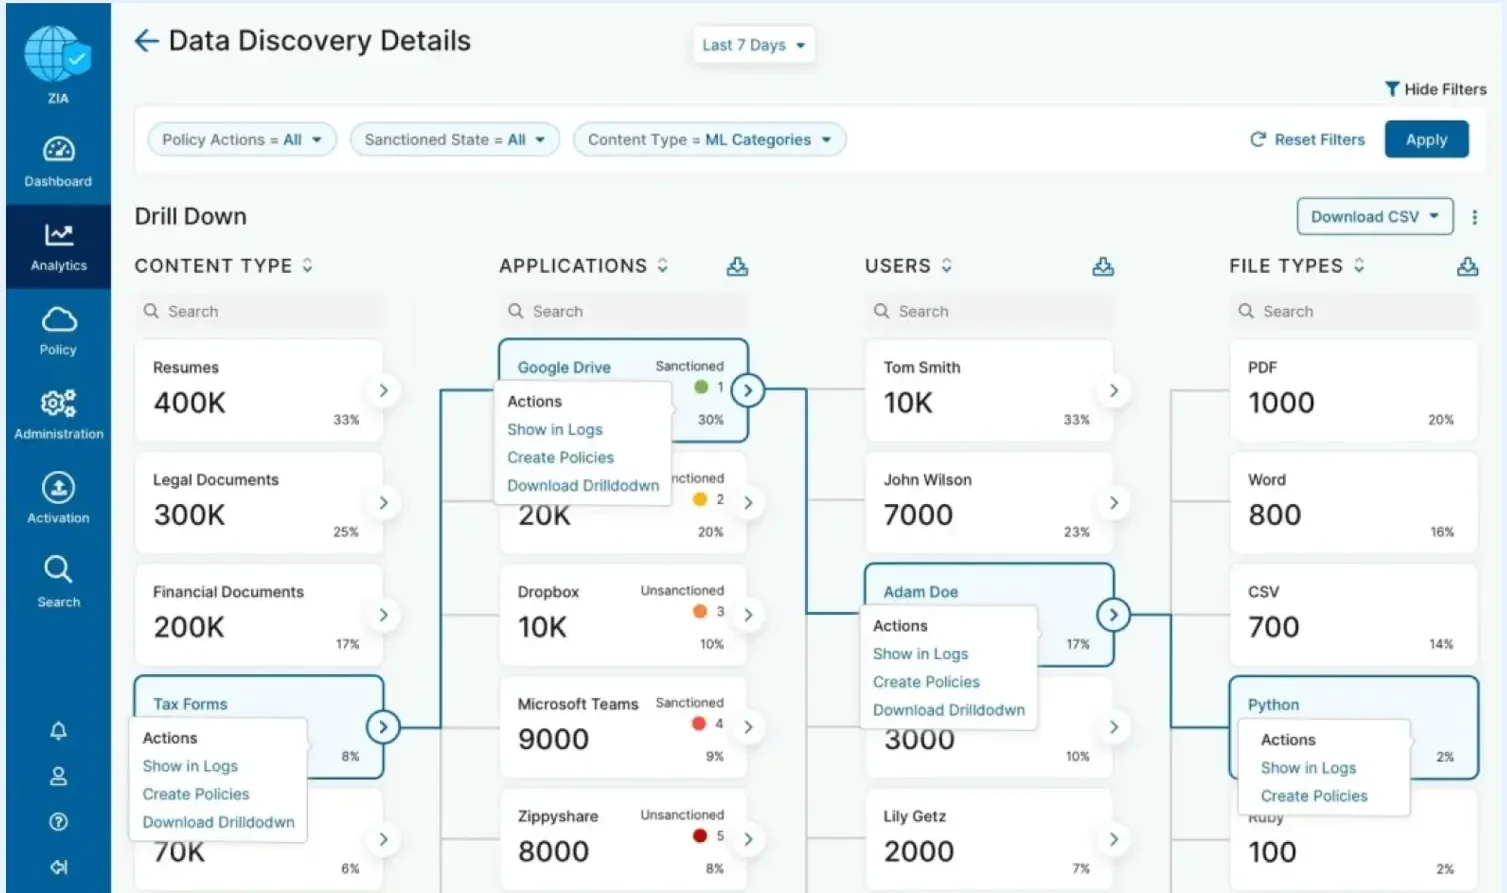
Best for: Distributed enterprises securing information across web traffic, SaaS applications, endpoints, and email.
Zscaler combines DLP capabilities with its cloud security infrastructure.
Inline Inspection
Zscaler can inspect supported traffic that passes through its security environment.
Policies can identify confidential information and allow or block selected activities according to destination, user, and content.
This is particularly useful for employees working across different locations without relying on a traditional office network.
Exact Data Match and Document Matching
Zscaler supports Exact Data Match and Indexed Document Matching.
Exact matching can identify protected structured records, while document matching helps detect known confidential files and document templates.
These techniques are useful when businesses need more precise identification than ordinary keywords.
OCR and Image Protection
Zscaler also provides OCR capabilities for detecting sensitive information contained in supported image files.
For example, information captured in a screenshot or scanned document may require protection even when it is not available as ordinary searchable text.
Endpoint and Email DLP
Zscaler extends its data security capabilities to supported endpoint and email workflows.
These controls complement inline cloud inspection by addressing information movement through additional channels.
Third-Party DLP Integration
Zscaler supports forwarding selected DLP information to external systems through ICAP.
However, the external system does not replace Zscaler’s own allow-or-block decision for the transaction. Enforcement remains governed by the configured Zscaler policy.
Business benefit: Zscaler provides coordinated DLP enforcement for organizations operating across distributed cloud environments.
Strengths: Inline inspection, exact matching, document fingerprinting, OCR, endpoint coverage, and centralized policies.
Limitations: Traffic routing, inspection configuration, product licensing, and supported integrations determine coverage.
6. TrueConf Server

Best for: Enterprises and public institutions that need secure corporate communication, private infrastructure, and integration with external DLP systems.
TrueConf Server is an on-premises communication platform combining corporate messaging, group chats, channels, file sharing, and video conferencing.
Unlike dedicated DLP platforms, TrueConf primarily provides a managed communication environment. Its relevance to data leakage prevention comes from organizational infrastructure control and ICAP-based DLP integration in TrueConf Enterprise.
Corporate Messaging and File Exchange
TrueConf supports direct messages, group chats, and channels for internal communication.
Employees can share documents, coordinate projects, and move from text conversations into video meetings without switching to unrelated services.
For example, an engineering company may use internal project chats to exchange product specifications and technical files rather than sending them through personal messaging accounts.
This makes corporate communication an important information protection boundary.
ICAP-Based DLP Integration
TrueConf Enterprise supports integration with external DLP systems through the Internet Content Adaptation Protocol (ICAP).
The integration allows supported text messages and files exchanged through corporate chats to be submitted for inspection before ordinary delivery.
The external DLP system evaluates the content against the organization’s security policies, and TrueConf handles it according to the configured response.
For example, a company can establish rules identifying confidential customer records or restricted documents in supported conversations.
The connected DLP engine performs the inspection. TrueConf provides the communication platform and inspection integration point.
Text Message Inspection
TrueConf allows administrators to configure how supported text messages are checked.
For unwanted messages, the system can replace the original content with text supplied by the DLP service, display a custom notification, or leave the original message unchanged.
The last configuration records the violation without preventing ordinary delivery.
Therefore, enabling message inspection does not automatically guarantee that all policy violations will be blocked. Administrators must verify the selected enforcement action.
File Inspection
TrueConf provides separate settings for files transferred through supported chats.
Administrators can configure inspection requests and handling rules for unwanted attachments.
This is useful when employees exchange financial reports, engineering documents, or other confidential files through business conversations.
File inspection depends on the capabilities of the connected DLP engine and the integration configuration.
DLP Server Availability
TrueConf Enterprise allows administrators to define what happens when the DLP server does not respond.
A restrictive configuration can prevent normal delivery of unchecked messages, while a permissive configuration can maintain communication when inspection is unavailable.
The system also supports response timeouts and protected ICAP connections using TLS.
These controls are important because a failure in the inspection service should not produce an undefined security state.
Recipient Context
ICAP requests can include supported contextual information such as sender details, message identifiers, chat identifiers, and recipient information.
This may help a compatible DLP engine evaluate whether information is being shared within an appropriate conversation.
A restricted document could be acceptable in a small authorized project group but inappropriate in a broader corporate discussion.
The exact policy decision depends on the external DLP system.
On-Premises and Isolated-Network Deployment
TrueConf Server can be installed on Windows or Linux infrastructure controlled by the organization.
Its full licensed edition supports ordinary internal communication within suitable private or isolated networks without public internet access.
This is relevant to manufacturing companies, public institutions, research organizations, and enterprises with strict network requirements.
Identity Management and Collaboration
TrueConf integrates with Active Directory and LDAP, supporting centralized employee account administration.
The platform also includes video conferencing, screen sharing, presentations, and compatibility with supported SIP and H.323 equipment.
Depending on licensing, conferences can support up to 2,000 participants.
These capabilities allow organizations to combine messaging and meetings within a managed corporate communication environment.
Practical Application
Consider an industrial organization operating several facilities through a private network.
Employees use TrueConf for engineering discussions, operational messaging, and file exchange.
The company connects a compatible DLP product to TrueConf Enterprise through ICAP and configures inspection for supported messages and attachments.
Administrators verify that restricted content is blocked when required and define fallback behavior if the DLP system becomes unavailable.
This extends data leakage prevention into corporate communication while leaving other channels, such as email and removable storage, to separate security controls.
Business benefit: TrueConf allows organizations to integrate corporate messaging into a broader information protection strategy while maintaining direct control over communication infrastructure.
Strengths: On-premises deployment, corporate chats, file exchange, ICAP-based DLP integration, configurable responses, identity integration, and video collaboration.
Limitations: TrueConf is not a standalone DLP solution. Inspection requires the appropriate enterprise edition and a compatible external DLP system.
Boost your team’s security with TrueConf Server Free!
7. Symantec Data Loss Prevention by Broadcom
Best for: Large organizations requiring established enterprise DLP capabilities across endpoints, networks, and supported cloud environments.
Symantec DLP combines content identification, policy administration, monitoring, and incident management.
Advanced Content Detection
Symantec supports techniques for recognizing structured and unstructured sensitive information.
These include exact data matching, document matching, and policy-based content analysis.
For example, a financial institution can protect actual customer records while reducing alerts caused by unrelated documents containing similar data patterns.
Endpoint and Network Protection
Symantec provides endpoint controls for supported file transfers and user activities.
Its broader architecture also includes network monitoring and prevention components.
Organizations should distinguish components that observe policy violations from those that can stop transfers within the relevant communication path.
Data Discovery
Symantec can help identify sensitive information in supported repositories.
This is useful for finding forgotten copies of confidential documents and improving access or retention policies.
Centralized Incident Management
The Symantec Enforce environment provides centralized policy administration and incident investigation.
For example, consider a financial institution whose DLP system detects an attempted external transfer of customer records.
The relevant detection component can generate an incident associated with the matching policy. Security analysts can review available information through Enforce, examine the matched content, and assess the relevant transfer activity.
Investigators may discover that the employee used an incorrect recipient address, attempted an unauthorized export, or was completing a legitimate transfer that requires a policy exception.
Centralized incident management helps the organization distinguish these scenarios and document the response.
For larger enterprises, the benefit is consistent investigation across different departments and supported detection components rather than separate manual processes for every communication channel.
Response Rules
Symantec supports response-rule mechanisms for incident handling and supported remediation.
Depending on the integration, actions can include notifications, administrative workflows, or enforcement through compatible systems.
Security teams should test whether a selected action prevents an unauthorized transfer before completion or initiates remediation after detection.
Business benefit: Symantec provides a structured approach to managing enterprise information protection policies, investigations, and incident responses.
Strengths: Content detection, discovery, endpoint and network components, centralized management, and response rules.
Limitations: Deployment and integration can be complex, and not all detection components provide identical blocking capabilities.
8. Fortra Digital Guardian DLP
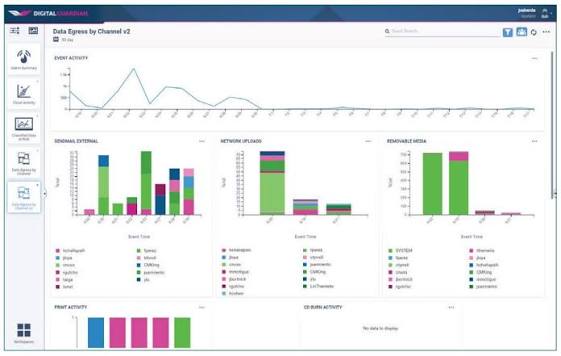
Best for: Businesses protecting intellectual property and sensitive information handled on employee endpoints.
Digital Guardian, now part of Fortra DLP, emphasizes endpoint visibility and contextual enforcement.
Endpoint Monitoring
Digital Guardian uses endpoint agents to record supported system, user, and data activities.
This helps organizations understand how sensitive files are accessed, modified, and transferred.
Monitoring can continue when managed devices operate outside the corporate network.
Context-Aware Controls
Administrators can configure supported actions such as logging, blocking, requesting justification, or encrypting sensitive information.
A research organization may allow engineers to edit confidential designs while preventing transfers to unauthorized removable devices.
Removable Media Protection
Digital Guardian provides granular restrictions for data transfers to removable media.
Policies may consider device characteristics, file classifications, and transfer conditions.
For example, a manufacturer may permit approved encrypted storage devices while restricting transfers to personal USB drives.
Intellectual Property Protection
Digital Guardian is particularly relevant to source code, research documents, engineering designs, and other information that may not contain conventional personal identifiers.
A semiconductor manufacturer can classify design files according to project sensitivity and establish controls over how those files are used on employee workstations.
An engineer working on an authorized project may continue editing the documents, while an attempt to copy classified designs to an unauthorized storage device triggers enforcement.
The classification must be meaningful to the organization. A file labeled Confidential should correspond to clear restrictions, approved destinations, and defined employee responsibilities.
Cloud Protection
Fortra’s broader DLP offerings include cloud data protection capabilities for supported repositories and applications.
These can complement endpoint controls by identifying sensitive information exposed through cloud storage.
Business benefit: Digital Guardian helps organizations protect commercially valuable information without indiscriminately blocking employee activity.
Strengths: Detailed endpoint visibility, contextual policies, removable media controls, classification, and intellectual property protection.
Limitations: Endpoint deployment requires agent administration and careful policy tuning.
9. Nightfall AI
Best for: SaaS-focused organizations needing automated sensitive data detection across collaboration applications and AI workflows.
Nightfall AI specializes in identifying confidential information within connected cloud applications.
SaaS Integrations
Nightfall provides integrations for supported services such as Slack, Google Drive, GitHub, Jira, and other business applications.
These integrations can identify sensitive information in messages, files, and application content.
Sensitive Data Detection
Nightfall uses automated classification to identify categories such as personal information, payment details, credentials, and secrets.
For example, a developer accidentally posting an API key in a collaboration channel may trigger an incident.
Slack Data Protection
Nightfall provides DLP capabilities for supported Slack environments.
It can identify sensitive content and apply configured actions such as redaction, deletion, or quarantine.
The available response depends on the application integration and permissions.
Detection vs. Remediation
Consider a developer who accidentally shares a production API credential in a Slack channel.
A connected DLP service may identify the credential and remove or redact the message according to the organization’s configured policy.
This reduces the period during which the secret remains visible. However, it does not necessarily mean that the original disclosure was prevented.
A credential may already have been viewed, copied, or captured before remediation occurs.
The appropriate security response may therefore also require credential rotation, an assessment of access logs, and investigation of possible misuse.
This illustrates an important distinction between detecting sensitive information, removing it from a collaboration platform, and eliminating the underlying security risk.
For other incidents, such as a confidential document shared through a cloud application, remediation may involve restricting permissions and informing the document owner.
Organizations should determine whether each integration provides inline blocking, post-event scanning, or both.
Developer APIs and AI Security
Nightfall also offers APIs for integrating sensitive data detection into custom applications.
Its broader capabilities include protection for supported generative AI workflows.
Business benefit: Nightfall extends automated classification and remediation into SaaS applications where employees frequently share sensitive information.
Strengths: Cloud integrations, automated detection, Slack protection, APIs, and AI-related security.
Limitations: Protection depends on supported applications, integration permissions, and whether inspection occurs before or after transfer.
10. Trellix Data Loss Prevention
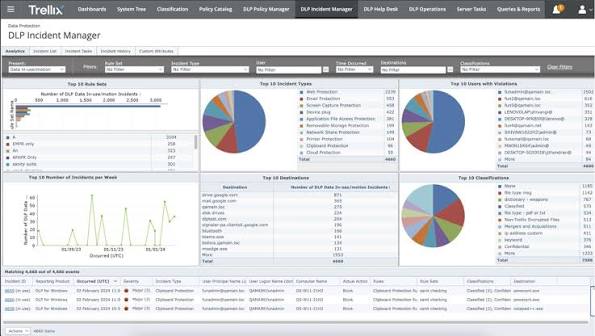
Best for: Organizations requiring granular endpoint protection, application-aware controls, and classification-based policies.
Trellix DLP includes endpoint-focused protection alongside additional network and discovery components.
Endpoint Protection
Trellix DLP Endpoint monitors supported file movement and application activity.
Administrators can configure restrictions for sensitive data transferred through removable storage and selected applications.
Application File Access Protection
Trellix provides Application File Access Protection capabilities that can restrict how classified files are accessed or transferred through supported applications.
For example, employees may be allowed to use an approved collaboration tool while being prevented from uploading certain restricted documents.
Microsoft Teams and Copilot Support
Trellix DLP Endpoint for Windows 11.14.1, released in November 2026, extends support to current Microsoft Teams and Copilot application formats.
The supported controls focus on classified file interactions, including defined file uploads and other application file movement scenarios.
This release does not provide universal monitoring or blocking of manually typed text in Teams or Copilot.
Certain clipboard operations are supported, but their coverage depends on the specific workflow and rule configuration.
Organizations should therefore test typed prompts, file uploads, and clipboard transfers separately.
Bluetooth and Device Controls
Trellix supports granular controls for selected Bluetooth file transfer scenarios.
Organizations can restrict unauthorized data transfers without necessarily disabling unrelated Bluetooth peripherals.
Classification and Rights Management
Trellix supports integrations with compatible data classification systems, including Fortra Boldon James Classifier.
Its product capabilities also include selected document labeling features and integration with Seclore Digital Rights Management.
These features help organizations apply restrictions to classified documents and supported external sharing workflows.
Network and Discovery Capabilities
Additional Trellix components address supported network DLP and data discovery requirements.
These functions must be evaluated separately from endpoint-only deployments.
Business benefit: Trellix helps organizations enforce classification-aware controls across managed endpoints and supported collaboration applications.
Strengths: Endpoint DLP, application file access protection, classification, device controls, and rights management integration.
Limitations: Capabilities vary by product component and release. Teams and Copilot support does not cover all text input scenarios.
Comparing Data Leakage Prevention Solutions
The ten products address different layers of information protection.
|
Solution |
Product category |
Main protection focus |
Distinctive capability |
|---|---|---|---|
|
Microsoft Purview DLP |
Enterprise DLP |
Microsoft 365, endpoints, and connected applications |
Integrated classification and enforcement |
|
Forcepoint DLP |
Enterprise DLP |
Endpoint, email, network, and cloud |
Risk-adaptive protection |
|
Netskope One DLP |
Cloud and enterprise DLP |
SaaS, web, cloud, and endpoints |
Inline and API-based inspection |
|
Proofpoint Enterprise DLP |
Enterprise DLP and insider risk |
Email, cloud, endpoints, and user activity |
Behavioral context |
|
Zscaler DLP |
Cloud and endpoint DLP |
Web, cloud, email, and endpoints |
Inline inspection and content matching |
|
TrueConf Enterprise |
Communication platform with DLP integration |
Corporate messaging and file exchange |
External DLP integration through ICAP |
|
Symantec DLP |
Enterprise DLP |
Endpoint, network, and discovery |
Centralized incident management |
|
Fortra Digital Guardian |
Endpoint-focused DLP |
Endpoint activity and intellectual property |
Contextual endpoint enforcement |
|
Nightfall AI |
SaaS and application DLP |
Collaboration tools and cloud services |
Automated detection and remediation |
|
Trellix DLP |
Endpoint and enterprise DLP |
Managed endpoints and applications |
Classification-aware file controls |
A dedicated DLP platform is not interchangeable with an application that supports DLP integration.
For example, TrueConf Enterprise can extend content inspection into supported corporate messaging workflows, while a separate DLP product may be responsible for classification, policy evaluation, and protection across additional channels.
Insight 3.
Approved applications can still be major data leakage channels.
A company may approve Microsoft Teams, Slack, Google Drive, or an internal communication platform because it meets corporate security requirements.
However, an approved application does not guarantee that every action performed within it is appropriate.
An employee may upload a confidential file to the wrong project workspace, invite an unauthorized external participant, or paste customer information into a broadly accessible channel.
Traditional controls that simply allow or block an application cannot always distinguish these situations.
Data leakage prevention should evaluate the information, recipient, permissions, and intended activity inside approved applications.
This is why application-level DLP and collaboration security policies are important even in organizations with strong endpoint and network protection.
How to Implement a Data Leakage Prevention Program?
A successful DLP implementation follows a structured process rather than deploying every available control simultaneously.
|
Phase |
Main activities |
Expected outcome |
|---|---|---|
|
1. Assessment |
Identify critical data and high-risk workflows |
Data inventory and risk priorities |
|
2. Classification |
Define sensitivity levels and owners |
Consistent information handling rules |
|
3. Policy design |
Establish approved users, destinations, and responses |
Documented DLP policies |
|
4. Pilot deployment |
Test rules in selected departments |
Validated detection and enforcement |
|
5. Rollout |
Expand coverage across systems and users |
Operational DLP controls |
|
6. Optimization |
Review incidents, false positives, and exceptions |
Continuous improvement |
Start With a High-Risk Business Process
A finance department sending confidential reports to external partners may provide a better initial use case than attempting to control every application used across the company.
The organization can identify the relevant data, approved recipients, and expected transfer channels. It can then test whether the DLP system distinguishes legitimate sharing from prohibited disclosure.
Once this process is reliable, the same approach can be extended to additional departments.
Validate Enforcement Before Scaling
A useful pilot should test both prohibited and authorized transfers.
For example, administrators can verify that a restricted spreadsheet cannot be uploaded to personal cloud storage while confirming that approved sharing with an authorized partner still works.
Tests should also include situations where the DLP engine becomes unavailable or a supported application changes its behavior.
This helps identify whether protection remains effective during failures and upgrades.
Define Program Ownership
Security teams manage technical controls, but business owners should determine which information is sensitive and which transfers are legitimate.
IT teams maintain endpoints, applications, and integrations. Legal and compliance specialists help interpret applicable requirements.
This separation of responsibilities reduces the risk of security rules being designed without understanding how employees actually work.
How to Measure Data Leakage Prevention Effectiveness?
DLP success should be measured through prevention outcomes, not merely deployment coverage or alert volume.
|
Metric |
What it measures? |
Why it matters? |
|---|---|---|
|
Pre-transfer block rate |
Percentage of tested prohibited transfers stopped before completion |
Measures preventive effectiveness |
|
False positive rate |
Legitimate activities incorrectly flagged |
Shows policy accuracy |
|
Critical data coverage |
High-value repositories and workflows protected |
Identifies visibility gaps |
|
Mean investigation time |
Time needed to evaluate important incidents |
Measures operational efficiency |
|
Policy override rate |
Frequency of permitted exceptions |
Indicates possible friction or policy mismatch |
|
Unmanaged application exposure |
Sensitive activity through unapproved services |
Highlights shadow IT and AI risks |
|
DLP service availability |
Ability to inspect transfers during normal and degraded operation |
Identifies reliability risks |
Organizations should establish baseline measurements before changing policies and then review performance at regular intervals.
For example, a decline in false positives is beneficial only if the revised policy continues to stop genuinely prohibited transfers. Likewise, expanding coverage to more applications matters when those integrations protect relevant information rather than simply increase the number of monitored services.
A useful DLP report should show both successful controls and unresolved gaps. Where the organization cannot directly measure a real-world prevention rate, it can use repeatable controlled tests for selected transfer scenarios and clearly distinguish those results from production incidents.
Insight 4.
A lower alert count can indicate a stronger DLP program.
Security teams often associate a higher number of alerts with improved monitoring.
But thousands of low-value notifications can consume analyst time and obscure serious incidents.
More accurate classification and contextual enforcement may reduce alert volume while improving prevention.
For example, a system that identifies every appearance of a financial term may generate more alerts than one that recognizes actual confidential financial records. Yet the second approach may produce better protection with less disruption.
The strongest DLP programs prioritize prevented exposure, high-confidence incidents, and sustainable policy enforcement over the total number of alerts.
This makes continuous tuning an essential part of information protection.
Common Data Leakage Prevention Mistakes
Organizations often encounter similar problems when introducing DLP, particularly when technical deployment advances faster than information governance.
Treating Every File as Equally Sensitive
Universal blocking policies create unnecessary restrictions and make legitimate collaboration difficult.
Classification and business context should determine protection requirements. A public marketing brochure does not need the same handling restrictions as an unpublished product design or a confidential customer database.
Protecting Email but Ignoring Collaboration Tools
Traditional DLP deployments often emphasize email and removable storage while providing weaker coverage for SaaS applications, corporate messaging, and AI tools.
Security teams should review the channels employees actually use and test whether existing policies inspect those activities.
Confusing Detection With Prevention
A policy alert does not establish that sensitive information was stopped before reaching its destination.
Organizations should verify whether the relevant enforcement point can block the activity and whether its rules are configured to do so.
Relying on DLP Instead of Access Governance
DLP cannot fully compensate for excessive permissions, compromised accounts, or weak administrative controls.
Identity management, endpoint security, and regular access reviews should operate alongside content inspection.
Leaving Policies Unchanged After Deployment
DLP policies may become outdated as applications, employee responsibilities, and business processes change.
A control that worked correctly during deployment may require adjustment after an application update or introduction of a new collaboration platform.
Regular validation helps identify these problems before they result in significant exposure.
Data Leakage Prevention Checklist for Enterprises
A DLP program is easier to assess when its controls have observable completion criteria. The following checklist focuses on evidence of implementation rather than general policy intentions.
|
Control |
Verification criterion |
|---|---|
|
Data discovery |
Critical repositories are inventoried, with named business owners and review dates |
|
Classification |
Priority datasets have approved sensitivity levels and documented handling rules |
|
Access management |
Permissions for high-risk repositories have been reviewed and unjustified access removed |
|
Endpoint protection |
Tests confirm that prohibited file transfers are blocked on supported managed devices |
|
Cloud security |
External sharing reports are reviewed and unauthorized public links are removed |
|
Corporate messaging |
Supported text and file transfer scenarios have documented inspection and enforcement results |
|
AI governance |
Approved AI services are listed, prohibited data categories are defined, and relevant workflows are tested |
|
Encryption |
Required device, storage, and transport encryption settings have been verified |
|
Employee awareness |
Relevant staff have completed scenario-based information handling training |
|
Incident response |
Investigators have defined procedures for triage, escalation, containment, and evidence handling |
|
DLP policy testing |
Controlled positive and negative test cases have been completed before broad enforcement |
|
Program reporting |
Regular reviews track blocked test transfers, false positives, coverage gaps, and assigned remediation actions |
This checklist should be adapted to the organization’s industry, infrastructure, risk tolerance, and legal obligations. Completion should be supported by configuration records, test results, review approvals, or other evidence rather than informal confirmation.
Conclusion
Data leakage prevention best practices focus on understanding sensitive information, controlling who can access it, and preventing inappropriate transfers across the systems employees use every day. The most important measures include data discovery, classification, least-privilege access, endpoint and cloud DLP, secure corporate messaging, AI usage policies, encryption, employee education, and continuous testing. Dedicated DLP platforms such as Microsoft Purview, Forcepoint, Netskope, and Proofpoint support different enforcement requirements, while communication platforms such as TrueConf Enterprise can extend external DLP inspection into supported corporate conversations.
The most effective data leakage prevention program is not necessarily the one with the largest number of tools or strictest blocking rules. It is the one that protects critical information without unnecessarily disrupting authorized work. Organizations should begin with high-risk data flows, validate controls against realistic scenarios, and measure how often prohibited transfers are actually prevented. As cloud collaboration and AI adoption expand, maintaining this protection requires regular policy reviews, updated integrations, and continued cooperation between security teams and business owners.
Empower your communication experience with TrueConf!
FAQ
What are the most important data leakage prevention best practices?
The most important practices are discovering and classifying sensitive information, enforcing least-privilege access, deploying DLP controls, securing endpoints and cloud applications, and monitoring unauthorized transfers. Organizations should also protect corporate messaging and AI workflows. Regular policy testing and employee training help ensure these controls remain effective.
How can a company prevent accidental data leakage?
Companies can reduce accidental leakage through classification labels, recipient verification, access restrictions, and DLP policies that warn or block employees before inappropriate transfers occur. Secure sharing defaults and practical employee training are also important. Policies should allow legitimate collaboration while restricting high-risk actions.
What is the difference between data leakage prevention and data loss prevention?
The terms are commonly used interchangeably in cybersecurity. Data leakage prevention emphasizes unauthorized disclosure, while data loss can also refer to information becoming unavailable or deleted. Commercial DLP platforms generally focus on monitoring and preventing unauthorized information access or transfer.
What are the three main types of DLP?
The traditional categories are endpoint DLP, network DLP, and cloud DLP. Endpoint DLP protects information on employee devices, network DLP monitors supported communication traffic, and cloud DLP secures information in SaaS applications and cloud environments. Many enterprise products combine these capabilities with email and application-level protection.
How can organizations prevent data leakage through generative AI?
Organizations should establish approved AI services, define which information employees may submit, and use AI-aware DLP to inspect supported prompts and uploads. Confidential source code, customer records, and regulated information should be restricted according to corporate policies. Technical controls should be supported by employee education and monitoring of unauthorized AI services.
Can DLP prevent confidential information from being shared through corporate messaging?
Yes, when the communication platform and DLP system support the required inspection and enforcement mechanisms. Microsoft Purview provides DLP capabilities for supported Teams messages, while TrueConf Enterprise can connect to compatible external DLP systems through ICAP. The ability to detect or block specific content depends on the application, configuration, and licensing.
How should businesses measure whether their DLP strategy works?
Businesses should evaluate how many prohibited transfers are blocked before completion, whether critical information is covered, and how frequently policies generate false positives. Incident resolution time, exceptions, and unmanaged application activity also provide useful indicators. Alert volume alone does not demonstrate effective data leakage prevention.
About the Author
Diana Shtapova is a product specialist and technology writer with three years of experience in the unified communications industry. At TrueConf, she leverages her deep product expertise to create clear and practical content on video conferencing platforms, collaboration tools, and enterprise communication solutions. With a strong background in product research and user-focused content development, Diana helps professionals and businesses understand core product features, adopt new technologies, and unlock the full potential of modern collaboration software.
Follow us on social networks